LexLint for security
You own the organization's exposure, and you already run a program that finds, tracks and closes vulnerabilities.
Read LexLint the way you read vulnerability management. The library is the legal CVE database, the lint is the scanner, and the portal is the ticketing workflow.
Portal
Manage exposure the way you manage vulnerabilities. Each finding becomes a work item with an owner, a status and a trail, and the counsel report is the evidence of what was decided and by whom.
How findings become work items
Lint
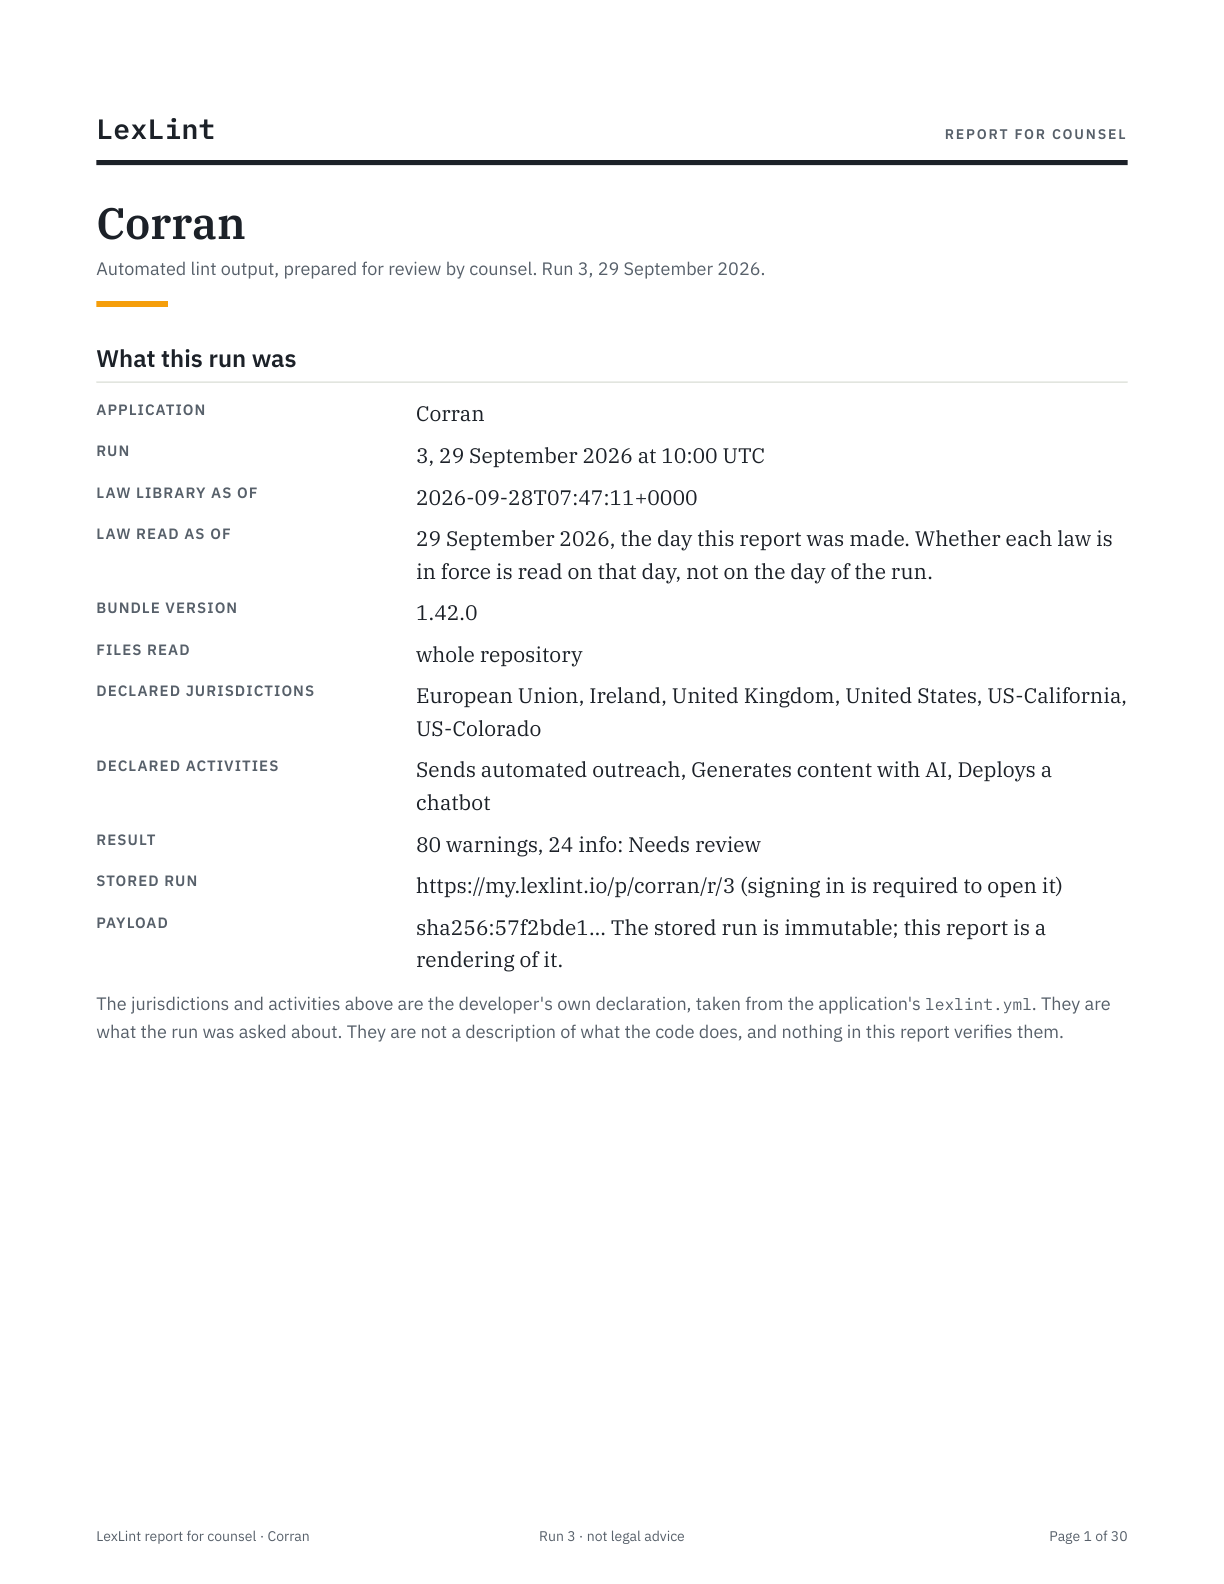
Identify exposure across your software and AI systems. Each run reads an app's declaration against the library and returns what applies, so a change to the app or to the law shows up in the next run.
Library
Evidence against the source. Every finding cites the provision and the date it was read, so the record shows which law a decision answered.
The result is legal information with citations, for your counsel to review. It is not legal review.
How findings become work items
Next: LexLint for legal teams. All four readers: Who it's for.