A law lint for your code.

Lint your app against the law it answers to. Free.

Claude Code, Codex, or any other coding agent declares what the app does and where it operates. That declaration is the whole input: no source code, schema, or data is uploaded. LexLint returns findings: which obligations apply in each jurisdiction, with citations and freshness dates. It catches the basics early. It is not legal review.

Paste the first line into the agent you already have open. No install, no account, no key.

Some agents will not fetch a page, or will not act on one they fetched. and paste that instead.

declared
generates_content, crawls_web
operates
EU, Canada, US-California
law library
WARNEU AI Act, Article 50since Providers of AI systems that interact directly with people must ensure users are informed they are dealing with an AI system unless obvious from context, and providers of generative AI must mark synthetic audio, image, video, or text output in a machine-readable, detectable format.read against its source
WARNCanada Uber Technologies Inc. v. Hellersince The joint reasons held that unconscionability requires both an inequality of bargaining power and a resulting improvident bargain.read against its source
WARNUS-California SB 942since A covered provider must make a disclosure verification tool available at no cost to the user, one that lets a user assess whether image, video, or audio content was created or altered, other than by a minor modification, by the provider's generative AI system and that outputs any system provenance data detected in the content.read against its source , for counsel

3 findings: 2 for code, 1 for counsel

A real run on today's LexLint law library, against a declaration of two activities and three jurisdictions. See the whole run

Software law in the news

What changed in the law

LexLint sweeps the wire every day across every jurisdiction in the law library, keeps what is about software law, and files each story against a law and a jurisdiction. All 2,406 stories in the press →

You need LexLint if

  • You or your AI agent crawl, train on, or republish other sites' content.
  • AI writes any content your users see.
  • Your app holds personal data, voices, or faces.
  • Under-18s can reach your app, or you check that they can't.
  • Your app has users in more than one country.

One checked box is enough. Is the legal risk real?

I build the app.

Run it in the coding CLI you already have open, read the findings in the terminal, and fix the cheap things while the code is fresh. An account keeps every run and turns each finding into a work item.
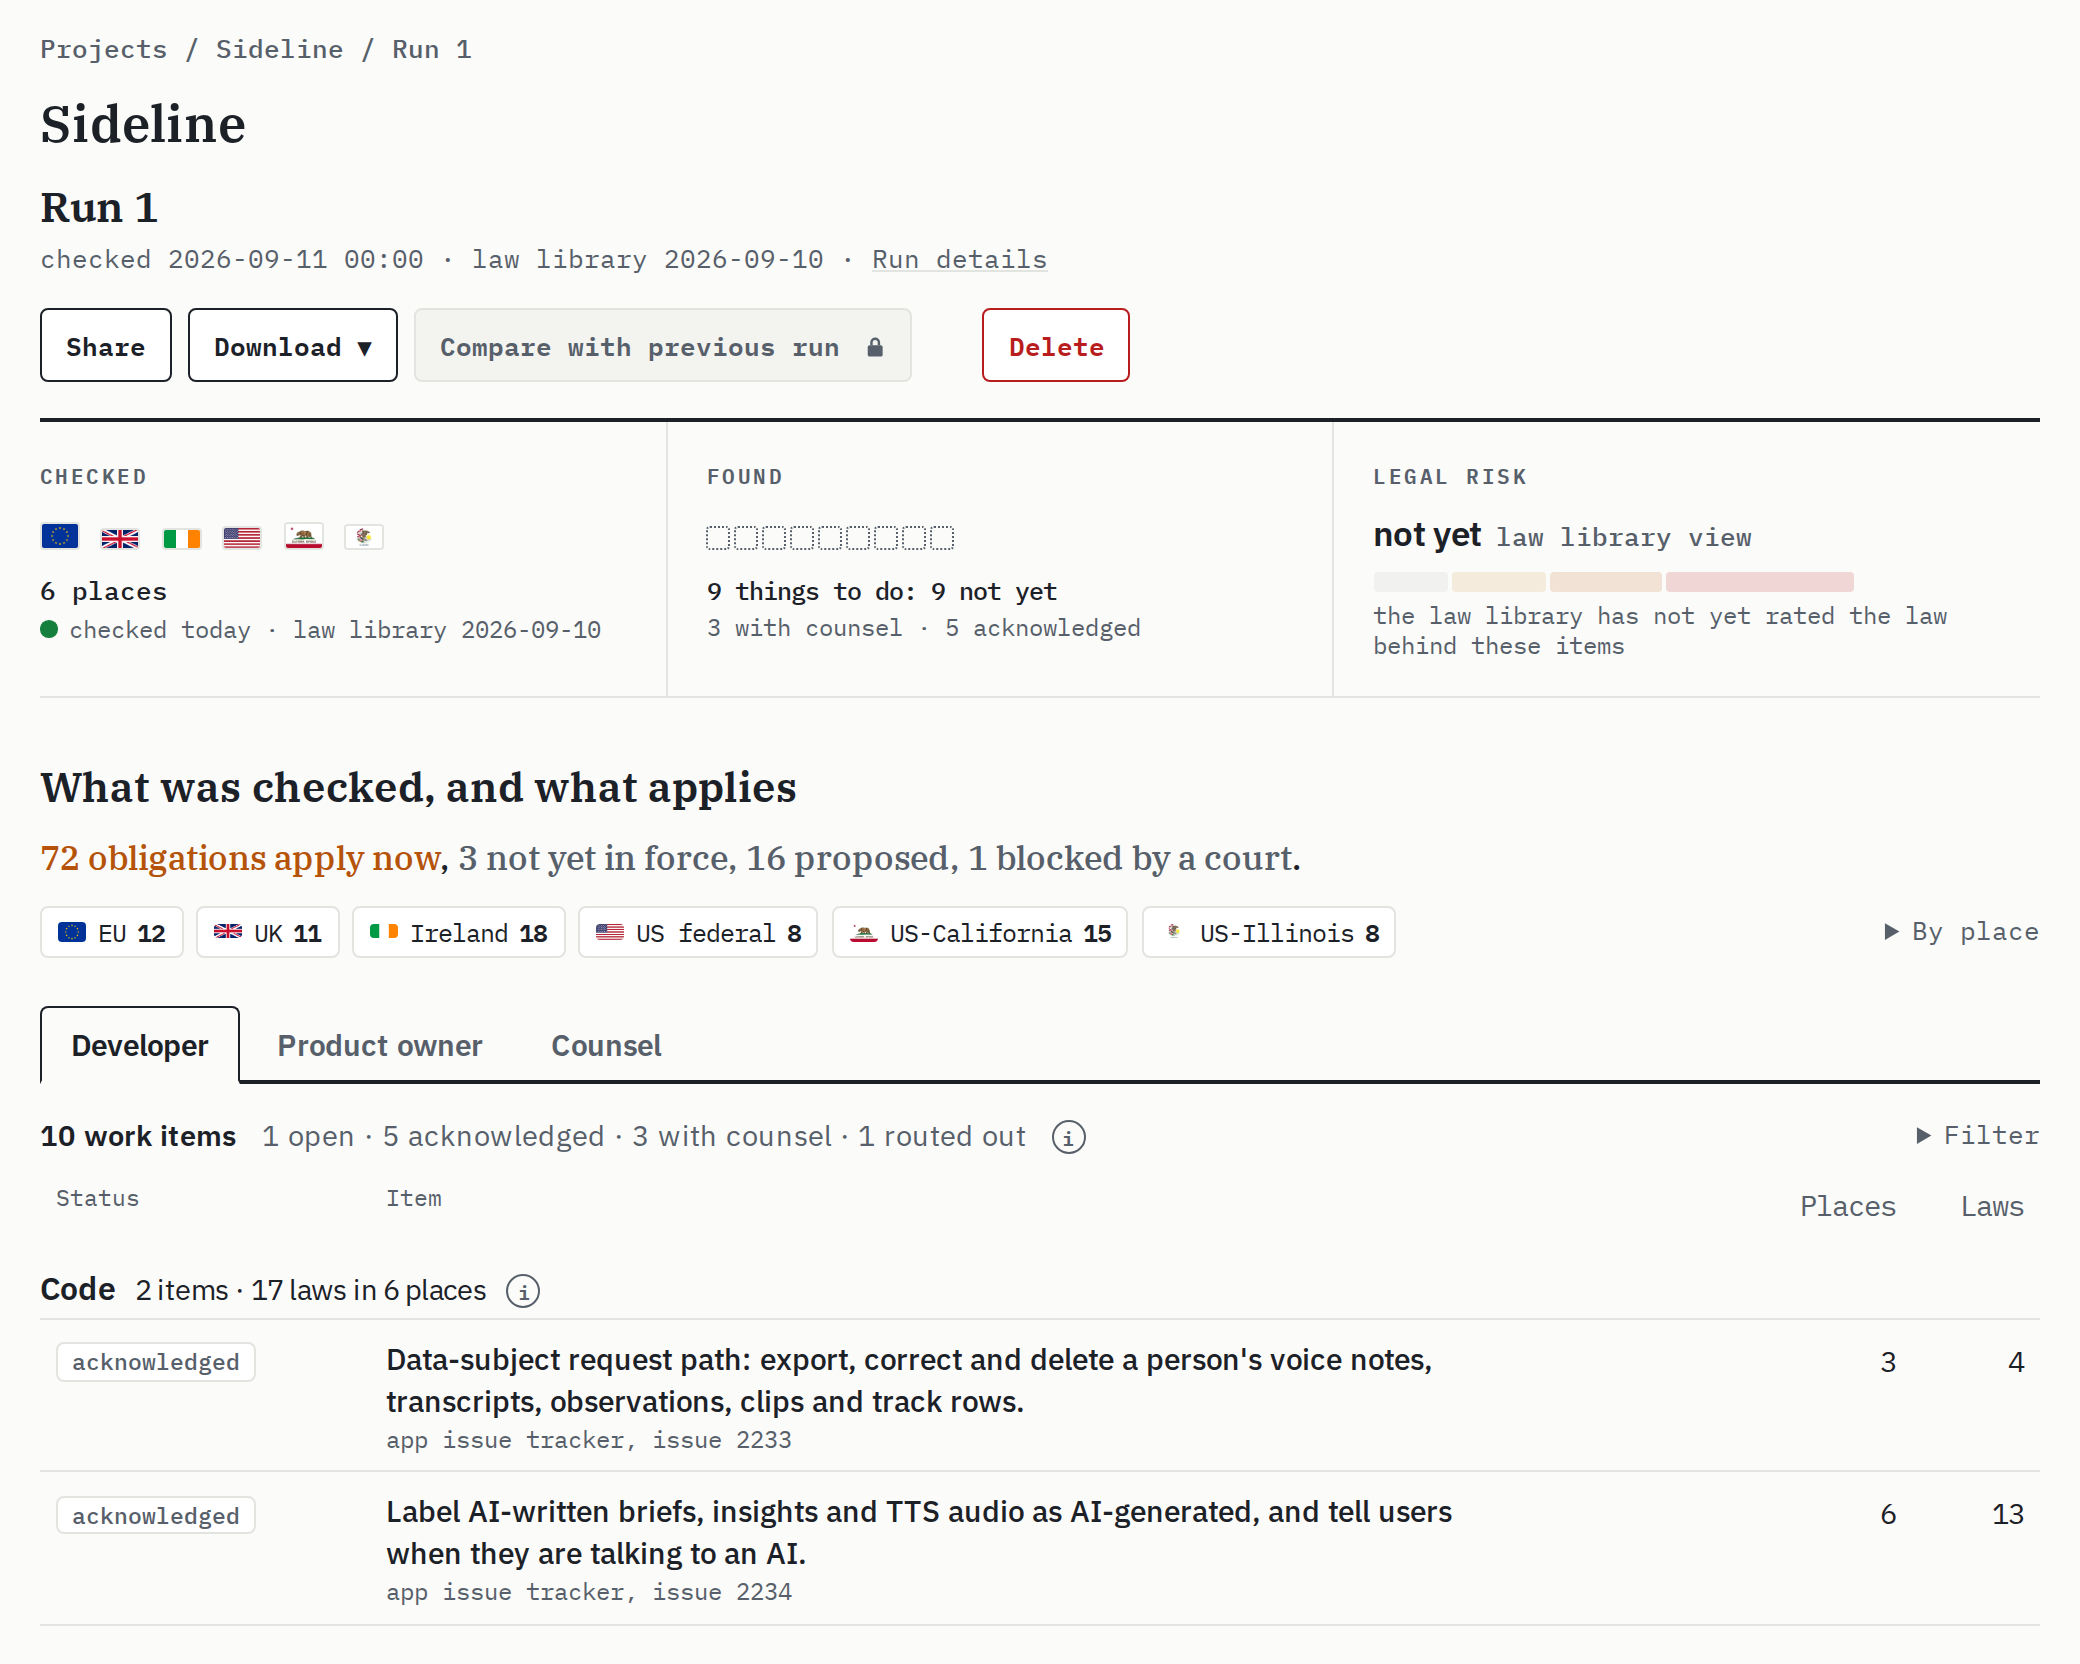
A run in the LexLint portal, developer view: six jurisdictions checked, nine things to do, three with counsel; 72 obligations apply now
What comes back in the portal: the run's findings as work items, one view per reader.

Building it and advising on it? Read the legal page first. It says what the product is for.

The clocks an incident starts

A breach, an exposed person's data, a service down: 561 instruments in 217 jurisdictions set a deadline, each with its own recipient and its own start. LexLint draws every deadline on a single time axis, one flag per clock.

Do you know what to do at each stage of your incident clock?

Sped up. The line is this moment on the drawing; the flags behind it are deadlines already reached.

Every reporting clock in the law library on one time axis, with SAFE's rungs beside them 682 marks in four lanes, one per instrument at each of its rungs: 197 in the first day, 331 in the first week, 124 in the first month, 30 in the first quarter. The axis is logarithmic from one hour to ninety days. Each mark is the flag of the jurisdiction whose law it is, and a link to that instrument's page, named by the jurisdiction, the law and the clock it sets. First day notifications First week notifications First month final reports First quarter notifications SAFE, 72 hours: notify customers with credible exposure SAFE, 4 business days: submit a confidential preliminary SAFE incident report SAFE, 14 days: issue a broader customer advisory when warranted SAFE, 30 days: publish a preliminary factual report, subject to security, legal and investigative constraints SAFE, 90 days: publish remediation status Security law Uruguay: Superintendencia de Servicios Financieros Communication on Technology, Systems and Information Security Events (30 minutes) United States: NRC cyber security event notifications by nuclear power plant licensees (1 hour) Brunei Darussalam: BDCB Notice on Cyber Intrusion and IT Incident Reporting by Banks (1 hour) China: National Cybersecurity Incident Reporting Measures (1 hour) China: People's Bank of China Cybersecurity Incident Reporting Measures, financial institution duties (1 hour) Singapore: MAS Notice FSM-N05, Report of Relevant Incidents by Banks (1 hour) Taiwan: Cyber Security Incident Reporting, Response and Drills Regulations, Specific Non-Government Agency Clocks (1 hour) Alberta: Alberta Reliability Standard CIP-008-AB-5, cyber security incident reporting and response planning (1 hour) Jordan: Cyber Security Law No. 16 of 2019, Article 8 private-sector incident-reporting and Center-cooperation duty (1 hour) Kuwait: Cyber and Operational Resilience Framework (CORF), Incident Reporting to the Central Bank of Kuwait (1 hour) Qatar: Qatar Central Bank Insurance Sector Cyber Security Regulation, incident management and reporting (1 hour) Qatar: Qatar Central Bank Technology Risks Regulation for Banks, incident management and reporting (1 hour) Belarus: Decree 40 On Cybersecurity: Cyber Incident Reporting to the National Cybersecurity Center (1 hour) Norway: Notification of Security Incidents by Electronic Communications Providers (1 hour) Solomon Islands: Central Bank of Solomon Islands Prudential Guideline No. 20 on Cybersecurity, Incident Notification to the Central Bank (60 minutes) Tonga: Prudential Banking Standard No. 15, Cybersecurity incident reporting by banks (60 minutes) Samoa: Commercial Banks Prudential Statements, Prudential Statement 11 on cybersecurity incident reporting (60 minutes) Georgia: Georgia Cyber Attack Reporting by Agencies (2 hours) Georgia: Georgia Cyber Attack Reporting by Utilities (2 hours) Utah: Safe Drinking Water Act, report of a security breach at a community water system (2 hours) Brunei Darussalam: BDCB Notice on Cyber Intrusion and IT Incident Reporting by Banks (2 hours) China: National Cybersecurity Incident Reporting Measures (2 hours) China: People's Bank of China Cybersecurity Incident Reporting Measures, financial institution duties (2 hours) Sri Lanka: Reporting of Information Technology and Cybersecurity Incidents of Licensed Banks (2 hours) Philippines: Manual of Regulations for Banks, Cyber Incident and Service Disruption Notification to the Bangko Sentral (2 hours) Singapore: Cybersecurity Act 2018, Report of Cybersecurity Incidents on Provider-Owned Critical Information Infrastructure (2 hours) Honduras: CNBS Norms on Information Technology, Information Security and Cybersecurity Management (Circular CNBS 025/2022), Incident Notification (2 hours) Rwanda: Regulation on Cyber Security in Regulated Institutions, Notification and Reporting of Cyber Incidents (2 hours) Eswatini: CBE Cybersecurity Guidelines for Financial Institutions No. 1 of 2021: Cyber Incident Notification (2 hours) Bahrain: Cyber Security Incident Reporting for Conventional Bank Licensees (Rulebook Volume 1, Module OM, Section OM-5.5) (2 hours) Bahrain: Cyber Security Incident Reporting for Crypto-Asset Licensees (Rulebook Volume 6, Module CRA, Section CRA-5.8) (2 hours) Bahrain: Cyber Security Incident Reporting for Insurance Licensees (Rulebook Volume 3, Module RM, Section RM-9.1) (2 hours) Bahrain: Cyber Security Incident Reporting for Investment Business Licensees (Rulebook Volume 4, Module RM, Section RM-9.1) (2 hours) Bahrain: Cyber Security Incident Reporting for Islamic Bank Licensees (Rulebook Volume 2, Module OM, Section OM-5.5) (2 hours) Israel: Directive 366, reporting of technological failures, data security incidents and cyber attacks (2 hours) Jordan: Cyber Security Law No. 16 of 2019, Article 8 private-sector incident-reporting and Center-cooperation duty (2 hours) Chile: Cybersecurity Incident Reporting Regulation under the Ley Marco de Ciberseguridad (3 hours) Chile: Ley Marco de Ciberseguridad, Reporting of Cybersecurity Incidents (3 hours) Ghana: Bank of Ghana Cyber and Information Security Directive, Incident Reporting (3 hours) North Macedonia: Law on Security of Network and Information Systems, Significant Incident and Threat Notification (3 hours) European Union: Commission Delegated Regulation (EU) 2024/1366, Cybersecurity Network Code for Cross-Border Electricity Flows: Information Sharing on Cyber-Attacks and Threats (4 hours) European Union: DORA, Article 19 (reporting of major ICT-related incidents), with the time limits of Delegated Regulation (EU) 2025/301 (4 hours) United States: NRC cyber security event notifications by nuclear power plant licensees (4 hours) China: National Cybersecurity Incident Reporting Measures (4 hours) Barbados: Technology and Cyber Risk Management Guideline, Classification and Reporting of Major Incidents to the Central Bank (4 hours) Barbados: Technology and Cyber Risk Management Guideline, Reporting of Cyber Incidents to the Financial Services Commission (4 hours) Angola: BNA Aviso 08/2020, Notification of Cyber Incidents to the Banco Nacional de Angola (4 hours) Nigeria: NCC Cyber Resilience Framework for the Nigerian Communication Sector, Cyber Incident Reporting to NCC-CSIRT (4 hours) United Arab Emirates: Operational Risk Management Regulation, notification of significant events and high-risk Incidents (4 hours) Israel: Directive 366, reporting of technological failures, data security incidents and cyber attacks (4 hours) Jordan: Cyber Security Law No. 16 of 2019, Article 8 private-sector incident-reporting and Center-cooperation duty (4 hours) Kuwait: Cyber and Operational Resilience Framework (CORF), Incident Reporting to the Central Bank of Kuwait (4 hours) Albania: Law On Cybersecurity, Incident Reporting by Operators of Critical and Important Information Infrastructure (4 hours) Vatican City: Payment Services Major Incident Notification (4 hours) Kosovo: Central Bank Regulation on Information Systems and Cyber Risk Management, Incident Reporting (4 hours) Cyprus: Security of Networks and Information Systems Law, Incident Notification Obligations (6 hours) Romania: Ordonanța de urgență nr. 155/2024, Incident Notification (6 hours) New Jersey: Board of Public Utilities Order on Utility Cyber Security Program Requirements, incident reporting (6 hours) India: CERT-In Cyber Security Directions, Incident Reporting, Logging and Time Synchronisation (6 hours) India: RBI Commercial Banks Cybersecurity Directions, Cyber Incident Reporting (6 hours) India: Telecom Cyber Security Rules, Reporting of Security Incidents (6 hours) United States: NRC cyber security event notifications by nuclear power plant licensees (8 hours) Botswana: Cybersecurity Act, Reporting of Cybersecurity Incidents (8 hours) Israel: Directive 366, reporting of technological failures, data security incidents and cyber attacks (8 hours) Florida: Local Government Cybersecurity Act, cybersecurity incident and ransomware reporting (12 hours) Florida: State Cybersecurity Act, state agency cybersecurity incident and ransomware reporting (12 hours) Kansas: Kansas Cybersecurity Act, notification of a significant cybersecurity incident by a public entity or government contractor (12 hours) Australia: Security of Critical Infrastructure Act, Notification of Cyber Security Incidents (12 hours) Hong Kong: Protection of Critical Infrastructures (Computer Systems) Ordinance, Incident Notification (12 hours) Zambia: Cyber Security Act, Reporting of Cyber Security Incidents (12 hours) European Union: Cyber Resilience Act, Manufacturer Reporting Obligations (24 hours) European Union: DORA, Article 19 (reporting of major ICT-related incidents), with the time limits of Delegated Regulation (EU) 2025/301 (24 hours) European Union: NIS2 Directive, Reporting Obligations (24 hours) European Union: eIDAS Regulation, Article 19a(1)(b): Notification of Security Breaches and Disruptions by Non-Qualified Trust Service Providers (24 hours) Austria: Netz- und Informationssystemsicherheitsgesetz 2026 (NISG 2026), Significant-Incident Reporting Obligations (24 hours) Belgium: Loi du 26 avril 2024, Significant-Incident Notification Obligations (24 hours) Bulgaria: Cybersecurity Act, Incident and Cyber-Threat Reporting Obligations (Zakon za kibersigurnost, ZKS) (24 hours) Cyprus: Security of Networks and Information Systems Law, Incident Notification Obligations (24 hours) Czech Republic: Cybersecurity Act (Zákon o kybernetické bezpečnosti), Incident Notification (24 hours) Germany: BSI-Gesetz (BSIG), Incident Notification (24 hours) Denmark: Act on Security and Preparedness in the Telecoms Sector (Lov om sikkerhed og beredskab i telesektoren), Significant Incident Notification (24 hours) Denmark: NIS 2-loven, Significant-Incident Reporting and Recipient-Notice Duties (24 hours) Estonia: Küberturvalisuse seadus (KüTS), Duty to Notify of a Cyber Incident (24 hours) Spain: Anteproyecto de Ley de Coordinación y Gobernanza de la Ciberseguridad, Incident Reporting Obligations (24 hours) Spain: Real Decreto-ley 12/2018, Incident Notification Obligation (24 hours) Finland: Kyberturvallisuuslaki, Significant-Incident Reporting Obligations (24 hours) France: Projet de loi Résilience des Infrastructures Critiques et Cybersécurité, Incident Notification (NIS2) (24 hours) Greece: Law 5160/2024, Significant-Incident Reporting Obligations (24 hours) Croatia: Zakon o kibernetičkoj sigurnosti and Uredba o kibernetičkoj sigurnosti, Incident and Cyber-Threat Reporting Obligations (24 hours) Hungary: Cybersecurity Act, Incident Notification and Cybersecurity Fine (24 hours) Ireland: National Cyber Security Bill, Incident Response Powers and Reporting Obligations (24 hours) Italy: Decreto Legislativo 4 settembre 2024, n. 138 (Decreto NIS2), Incident Notification (24 hours) Italy: Legge 28 giugno 2024, n. 90, Incident Notification and Vulnerability Remediation Duties (24 hours) Lithuania: Kibernetinio saugumo įstatymas (Law on Cyber Security), Incident Notification (24 hours) Luxembourg: Loi du 5 mai 2026 relative à la cybersécurité (NIS2), Incident Notification (24 hours) Latvia: Nacionālās kiberdrošības likums, Incident Notification (24 hours) Malta: Measures for a High Common Level of Cybersecurity across the European Union (Malta) Order, Significant-Incident Reporting to the National CSIRT (24 hours) Netherlands: Cyberbeveiligingswet, Significant-Incident Reporting Obligations (24 hours) Poland: Ustawa o krajowym systemie cyberbezpieczeństwa (KSC), Zgłaszanie Incydentów Poważnych (24 hours) Portugal: Regime Jurídico da Cibersegurança, Significant-Incident Reporting Obligations (24 hours) Romania: Ordonanța de urgență nr. 155/2024, Incident Notification (24 hours) Sweden: Cybersäkerhetslag, Incident Notification (24 hours) Slovenia: Zakon o informacijski varnosti (ZInfV-1), Significant-Incident Notification Obligations (24 hours) Slovakia: Zákon o kybernetickej bezpečnosti (Cybersecurity Act), Incident and Vulnerability Notification (24 hours) United States: Cyber Incident Reporting for Critical Infrastructure Act of 2022 (CIRCIA) (24 hours) United States: NRC cyber security event notifications by nuclear power plant licensees (24 hours) United States: SEC Regulation SCI: notification of SCI events to the Commission and to members (24 hours) Indiana: Public water and wastewater cybersecurity: incident reporting to the Office of Technology (24 hours) Louisiana: Clerk of court, notification of cyber incidents to the secretary of state (24 hours) Maryland: Maryland public service company duty to report a cybersecurity incident to the State Security Operations Center (24 hours) New Mexico: Cybersecurity incident reporting order for agencies and political subdivisions (24 hours) Nevada: Governor's Technology Office, reporting of suspected cybersecurity incidents by a using agency (1 business day) New York: Cybersecurity incident reporting by municipal corporations and public authorities (24 hours) New York: New York Department of Financial Services Cybersecurity Regulation, Notices to the Superintendent (24 hours) Rhode Island: Municipal and state agencies, notification of a cybersecurity incident to the state police (24 hours) Tennessee: Utility cybersecurity incident notification to the Tennessee Public Utility Commission (24 hours) Virginia: Public bodies: incident reporting to the Virginia Fusion Intelligence Center (24 hours) Washington: Major cybersecurity incidents: state agency reporting to the office of cybersecurity (24 hours) China: Network Data Security Management Regulation, product vulnerability and incident reporting (24 hours) China: People's Bank of China Cybersecurity Incident Reporting Measures, financial institution duties (24 hours) Fiji: Reserve Bank of Fiji Prudential Supervision Policy Statement 2, Cybersecurity Incident Reporting (24 hours) Indonesia: OJK Regulation on Information Technology in Commercial Banks, Reporting of IT and Cyber Incidents (24 hours) Indonesia: Presidential Regulation 82 of 2022, reporting of cyber incidents on vital information infrastructure (24 hours) Papua New Guinea: Cybersecurity Bill 2026, Incident Reporting by CII Operators and Financial Institutions (24 hours) Papua New Guinea: Cybersecurity Bill 2026, Mandatory Incident Reporting by Any Entity (24 hours) Philippines: Manual of Regulations for Banks, Cyber Incident and Service Disruption Notification to the Bangko Sentral (24 hours) Vietnam: Circular on Information System Security in Banking Operations, Incident Reporting to the State Bank (24 hours) Barbados: Technology and Cyber Risk Management Guideline, Classification and Reporting of Major Incidents to the Central Bank (24 hours) Barbados: Technology and Cyber Risk Management Guideline, Reporting of Cyber Incidents to the Financial Services Commission (24 hours) Chile: Cybersecurity Incident Reporting Regulation under the Ley Marco de Ciberseguridad (24 hours) Mexico: CNBV and Banco de México Provisions for Electronic Payment Funds Institutions, Information Security Incident Reporting (24 hours) Nicaragua: Technology Risk Management Norm, Information to the Superintendent on Security Incidents (24 hours) Paraguay: Trust Services Law, Security Breach Notification by Trust Service Providers (24 hours) Trinidad and Tobago: Cybersecurity Best Practices Guideline, Notification of Cybersecurity Incidents to the Central Bank (24 hours) Uruguay: Decreto 66/025, Cybersecurity Incident Reporting to CERTuy (24 hours) Uruguay: Ley 20.212, Cybersecurity Incident Reporting by Public and Critical-Sector Entities (24 hours) Benin: Digital Code: Trust Service Provider Security-Breach Notification (24 hours) Democratic Republic of the Congo: Digital Code, Livre II: Trust Service Provider Security-Incident Notification (24 hours) Ghana: Bank of Ghana Cyber and Information Security Directive, Incident Reporting (1 business day) Ghana: Critical Information Infrastructure Directive, Incident and Vulnerability Reporting (24 hours) Ghana: Cybersecurity Act, Critical Information Infrastructure Owner's Incident Report (24 hours) Ghana: Cybersecurity Act, Duty to Report Cybersecurity Incident (24 hours) Kenya: Computer Misuse and Cybercrimes Act, Reporting of Cyber Threat (24 hours) Kenya: Critical Information Infrastructure Regulations, Incident Reporting by an Owner (24 hours) Kenya: Virtual Asset Service Providers Regulations, Reporting of Cybersecurity Incidents (24 hours) Liberia: LTA Cybersecurity Regulations 2026: Incident Notification and Semiannual Reporting to the Liberia Telecommunications Authority (24 hours) Namibia: Bank of Namibia Determination of the Operational and Cybersecurity Standards within the National Payment System (PSD-12), Cyber Incident Reporting (24 hours) Namibia: Bank of Namibia Determination on Information Security (BID-30) of 2026, Incident Reporting (24 hours) Nigeria: CBN Risk-Based Cybersecurity Framework for Banks and Payment Service Banks, 2024, 24-Hour Cyber-Incident Report (24 hours) Nigeria: NCC Cyber Resilience Framework for the Nigerian Communication Sector, Cyber Incident Reporting to NCC-CSIRT (24 hours) Rwanda: Regulation on Cyber Security in Regulated Institutions, Notification and Reporting of Cyber Incidents (24 hours) Seychelles: Seychelles Virtual Asset Service Providers (Cyber Security Requirements) Regulations, 2024: Reporting of Cyber Security Risk (24 hours) Sierra Leone: Bank of Sierra Leone Cyber Security and IT Risk Management Guidelines for Commercial Banks: Cyber Security Incident and Threat Reporting (24 hours) Uganda: National Payment Systems Regulations, 2021, Electronic Money Issuer Incident Notification (24 hours) South Africa: SARB Directive on Cyber-Incident Reporting within the National Payment System (24 hours) United Arab Emirates: ADGM General Rulebook, notification of a material Cyber Incident (24 hours) United Arab Emirates: Operational Risk Management Regulation, notification of significant events and high-risk Incidents (24 hours) Jordan: Cyber Security Law No. 16 of 2019, Article 8 private-sector incident-reporting and Center-cooperation duty (24 hours) Andorra: Llei 22/2022, Incident Handling and Notification Obligation (24 hours) Antigua and Barbuda: Antigua and Barbuda Digital Assets Business Act 2020, Compliance Officer Report of a Cyber Reporting Event (1 day) Antigua and Barbuda: Antigua and Barbuda Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (24 hours) Albania: AKEP Regulation On Organisational and Technical Security Measures, Incident Reporting (24 hours) Armenia: Law on Cybersecurity: Cyber Incident Notification (24 hours) Switzerland: Mandatory Reporting of Cyberattacks on Critical Infrastructure (24 hours) Micronesia: FSM Cybersecurity Act 2025 (Bill), Critical Information Infrastructure Incident Reporting Clock (24 hours) Grenada: Grenada ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (24 hours) Kiribati: Cybersecurity Act 2026, Duty to Report a Cybersecurity Incident (24 hours) Saint Kitts and Nevis: Saint Kitts and Nevis Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (24 hours) Saint Lucia: Saint Lucia ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (24 hours) Liechtenstein: Cyber-Sicherheitsgesetz (CSG), Incident Notification (24 hours) Moldova: Law 48/2023 on Cybersecurity: Cyber Incident Notification (24 hours) Montenegro: Law on Information Security, Cyber Threat and Incident Reporting (24 hours) Marshall Islands: Cybersecurity Act 2025, Cybersecurity Incident Reporting Obligations (24 hours) North Macedonia: Law on Security of Network and Information Systems, Significant Incident and Threat Notification (24 hours) Norway: Incident Notification by Providers of Essential Societal Services and Digital Services (24 hours) Serbia: Law on Information Security, Incident Reporting Obligations (24 hours) Tonga: Cybersecurity Act 2025, Duty to Report a Cybersecurity Incident (24 hours) Saint Vincent and the Grenadines: Saint Vincent and the Grenadines Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (24 hours) Kosovo: Law No. 08/L-173 on Cyber Security, Incident Reporting and Enforcement (24 hours) United States: Computer-Security Incident Notification Requirements for Banking Organizations and Their Bank Service Providers (36 hours) Texas: Texas state bank regulation, notice of a computer-security incident to the banking commissioner (36 hours) Taiwan: Cyber Security Incident Reporting, Response and Drills Regulations, Specific Non-Government Agency Clocks (36 hours) Spain: Real Decreto-ley 12/2018, Incident Notification Obligation (48 hours) Croatia: Zakon o kibernetičkoj sigurnosti and Uredba o kibernetičkoj sigurnosti, Incident and Cyber-Threat Reporting Obligations (48 hours) Florida: Local Government Cybersecurity Act, cybersecurity incident and ransomware reporting (48 hours) Florida: State Cybersecurity Act, state agency cybersecurity incident and ransomware reporting (48 hours) Indiana: Public water and wastewater cybersecurity: incident reporting to the Office of Technology (2 business days) Indiana: State agency and political subdivision cybersecurity incident reporting to the Office of Technology (2 business days) Kentucky: Notification of a personal information security breach by public agencies to state officials (48 hours) Puerto Rico: Government Cybersecurity Act, incident reporting to the Puerto Rico Innovation and Technology Service (48 hours) Texas: Texas Cyber Command, cybersecurity incident notification by a state agency or local government (48 hours) China: Network Product Security Vulnerability Management Provisions, product provider duties (2 days) Hong Kong: Protection of Critical Infrastructures (Computer Systems) Ordinance, Incident Notification (48 hours) Kyrgyzstan: Digital Code, digital resilience incident notification (48 hours) Honduras: CNBS Norms on Information Technology, Information Security and Cybersecurity Management (Circular CNBS 025/2022), Incident Notification (2 business days) Mexico: CNBV General Provisions for Credit Institutions, Information Security Incident Reporting (48 hours) Peru: Regulation of the Digital Trust Framework (Supreme Decree 126-2025-PCM), Notification of Digital-Security Incidents (48 hours) Ethiopia: Critical Infrastructure Cybersecurity Proclamation, Cyber Incident Reporting to National CERT (48 hours) Ethiopia: Requirements for Information Technology (IT) Management Directive, IT Incident Reporting (2 business days) Ethiopia: Requirements for Information Technology (IT) Management of Banks Directive, IT Incident Reporting (2 business days) South Africa: SARB Directive on Cyber-Incident Reporting within the National Payment System (48 hours) Antigua and Barbuda: Antigua and Barbuda Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (48 hours) Armenia: Law on Cybersecurity: Cyber Incident Notification (2 days) Grenada: Grenada ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (48 hours) Saint Kitts and Nevis: Saint Kitts and Nevis Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (48 hours) Saint Lucia: Saint Lucia ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (48 hours) Saint Vincent and the Grenadines: Saint Vincent and the Grenadines Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (48 hours) European Union: Commission Delegated Regulation (EU) 2022/1645, External Reporting of Information Security Incidents and Vulnerabilities (IS.D.OR.230) (72 hours) European Union: Commission Implementing Regulation (EU) 2023/203, External Reporting of Information Security Incidents and Vulnerabilities in Aviation (IS.I.OR.230) (72 hours) European Union: Cyber Resilience Act, Manufacturer Reporting Obligations (72 hours) European Union: DORA, Article 19 (reporting of major ICT-related incidents), with the time limits of Delegated Regulation (EU) 2025/301 (72 hours) European Union: European Health Data Space Regulation, Serious-Incident Reporting by Manufacturers of EHR Systems (3 days) European Union: NIS2 Directive, Reporting Obligations (72 hours) Austria: Netz- und Informationssystemsicherheitsgesetz 2026 (NISG 2026), Significant-Incident Reporting Obligations (72 hours) Belgium: Loi du 26 avril 2024, Significant-Incident Notification Obligations (72 hours) Bulgaria: Cybersecurity Act, Incident and Cyber-Threat Reporting Obligations (Zakon za kibersigurnost, ZKS) (72 hours) Cyprus: Security of Networks and Information Systems Law, Incident Notification Obligations (72 hours) Czech Republic: Cybersecurity Act (Zákon o kybernetické bezpečnosti), Incident Notification (72 hours) Germany: BSI-Gesetz (BSIG), Incident Notification (72 hours) Denmark: Act on Security and Preparedness in the Telecoms Sector (Lov om sikkerhed og beredskab i telesektoren), Significant Incident Notification (72 hours) Denmark: NIS 2-loven, Significant-Incident Reporting and Recipient-Notice Duties (72 hours) Estonia: Küberturvalisuse seadus (KüTS), Duty to Notify of a Cyber Incident (72 hours) Spain: Anteproyecto de Ley de Coordinación y Gobernanza de la Ciberseguridad, Incident Reporting Obligations (72 hours) Spain: Real Decreto-ley 12/2018, Incident Notification Obligation (72 hours) Finland: Kyberturvallisuuslaki, Significant-Incident Reporting Obligations (72 hours) France: Projet de loi Résilience des Infrastructures Critiques et Cybersécurité, Incident Notification (NIS2) (72 hours) Greece: Law 5160/2024, Significant-Incident Reporting Obligations (72 hours) Croatia: Zakon o kibernetičkoj sigurnosti and Uredba o kibernetičkoj sigurnosti, Incident and Cyber-Threat Reporting Obligations (72 hours) Hungary: Cybersecurity Act, Incident Notification and Cybersecurity Fine (72 hours) Ireland: European Union (NIS) Regulations 2018, Incident Notification (72 hours) Ireland: National Cyber Security Bill, Incident Response Powers and Reporting Obligations (72 hours) Italy: Decreto Legislativo 4 settembre 2024, n. 138 (Decreto NIS2), Incident Notification (72 hours) Italy: Legge 28 giugno 2024, n. 90, Incident Notification and Vulnerability Remediation Duties (72 hours) Lithuania: Kibernetinio saugumo įstatymas (Law on Cyber Security), Incident Notification (72 hours) Luxembourg: Loi du 20 décembre 2024, Cybersecurity Certification Authority and Vulnerability Notices (72 hours) Luxembourg: Loi du 5 mai 2026 relative à la cybersécurité (NIS2), Incident Notification (72 hours) Latvia: Nacionālās kiberdrošības likums, Incident Notification (72 hours) Malta: Gaming Authorisations and Compliance Directive, Notification of Information Security Breaches (3 business days) Malta: Measures for a High Common Level of Cybersecurity across the European Union (Malta) Order, Significant-Incident Reporting to the National CSIRT (72 hours) Netherlands: Cyberbeveiligingswet, Significant-Incident Reporting Obligations (72 hours) Poland: Ustawa o krajowym systemie cyberbezpieczeństwa (KSC), Zgłaszanie Incydentów Poważnych (72 hours) Portugal: Regime Jurídico da Cibersegurança, Significant-Incident Reporting Obligations (72 hours) Romania: Ordonanța de urgență nr. 155/2024, Incident Notification (72 hours) Sweden: Cybersäkerhetslag, Incident Notification (72 hours) Slovenia: Zakon o informacijski varnosti (ZInfV-1), Significant-Incident Notification Obligations (72 hours) Slovakia: Zákon o kybernetickej bezpečnosti (Cybersecurity Act), Incident and Vulnerability Notification (72 hours) United Kingdom: Notification of Incidents by Operators of Essential Services (72 hours) United Kingdom: Notification of Incidents by Relevant Digital Service Providers (72 hours) United States: Cyber Incident Reporting for Critical Infrastructure Act of 2022 (CIRCIA) (72 hours) United States: NCUA Cyber Incident Notification Requirements for Federally Insured Credit Unions (72 hours) United States: SEC Regulation S-P: service provider oversight and 72-hour breach notice to the covered institution (72 hours) United States: Safeguarding Covered Defense Information and Cyber Incident Reporting (DFARS 252.204-7012) (72 hours) Alaska: Insurance Data Security, investigation and notification of a cybersecurity event (3 business days) Hawaii: Insurance Data Security Law, cybersecurity event investigation and notice to the commissioner (3 business days) Illinois: Insurance Data Security Law, investigation and notification of a cybersecurity event (3 business days) Kansas: Kansas Cybersecurity Act, notification of a significant cybersecurity incident by a public entity or government contractor (72 hours) Kentucky: Notification of a personal information security breach by public agencies to state officials (72 hours) Maine: Maine Insurance Data Security Act, notice of a cybersecurity event to the superintendent (3 business days) Minnesota: Minnesota Insurance Data Security Act, notification of a cybersecurity event to the commissioner (3 business days) Minnesota: Minnesota cybersecurity incident reporting by public agencies and government contractors (72 hours) Missouri: Insurance Data Security Act: notice of a cybersecurity event to the director (3 business days) Mississippi: Data Security for Money Transmitters Act, notice of a notification event to the Commissioner (72 hours) Mississippi: Insurance Data Security Law, investigation and notification of a cybersecurity event (3 business days) North Dakota: Insurance Data Security Law, investigation and notification of a cybersecurity event (3 business days) New Jersey: Cybersecurity incident reporting by public agencies and government contractors (72 hours) New York: Cybersecurity incident reporting by municipal corporations and public authorities (72 hours) New York: Hospital Cybersecurity Requirements, notice of a cybersecurity incident to the Department of Health (72 hours) New York: New York Department of Financial Services Cybersecurity Regulation, Notices to the Superintendent (72 hours) New York: Public Service Commission Information Technology Cybersecurity Requirements, notices to the Department (72 hours) Ohio: Ohio Insurance Data Security Law, cybersecurity event investigation and notice to the superintendent (3 business days) Puerto Rico: Cybersecurity Standards for the Insurance Industry, investigation of a cybersecurity incident and notice to the Commissioner within 72 hours (72 hours) Rhode Island: Licensed nonbank financial institutions, notification of a security event (3 business days) South Carolina: Insurance Data Security Act, investigation and notice of a cybersecurity event to the director (72 hours) Tennessee: Utility cybersecurity incident notification to the Tennessee Public Utility Commission (72 hours) Wisconsin: Insurance Data Security Law, investigation and notice of a cybersecurity event to the commissioner (3 business days) Australia: Prudential Standard CPS 234 Information Security, Notification to APRA (72 hours) Australia: Security of Critical Infrastructure Act, Notification of Cyber Security Incidents (72 hours) Kyrgyzstan: Digital Code, digital resilience incident notification (72 hours) Papua New Guinea: Cybersecurity Bill 2026, Mandatory Incident Reporting by Any Entity (72 hours) Singapore: Cybersecurity Act 2018, Report of Cybersecurity Incidents on Provider-Owned Critical Information Infrastructure (72 hours) Taiwan: Cyber Security Incident Reporting, Response and Drills Regulations, Specific Non-Government Agency Clocks (72 hours) Canada: Critical Cyber Systems Protection Act, Reporting of Cyber Security Incidents (72 hours) Ontario: Enhancing Digital Security and Trust Act, 2024, report of a critical cyber security incident by prescribed public sector entities (72 hours) Chile: Cybersecurity Incident Reporting Regulation under the Ley Marco de Ciberseguridad (72 hours) Jamaica: Standard of Sound Practice on Management of Cyber Risks, Reporting of Cyber Incidents and Data Breaches to the Bank of Jamaica (72 hours) Trinidad and Tobago: Cybersecurity Best Practices Guideline, Notification of Cybersecurity Incidents to the Central Bank (72 hours) Ghana: Critical Information Infrastructure Directive, Incident and Vulnerability Reporting (72 hours) Liberia: LTA Cybersecurity Regulations 2026: Incident Notification and Semiannual Reporting to the Liberia Telecommunications Authority (72 hours) Nigeria: Cybercrimes (Prohibition, Prevention, etc.) Act, 2015, as amended in 2024, Reporting of Cyber Threats to the National CERT (72 hours) South Africa: Cybercrimes Act, Duty to Report Cybercrime Offences to the Police (72 hours) United Arab Emirates: DFSA General Module, notification of a material Cyber Incident (72 hours) United Arab Emirates: Operational Risk Management Regulation, notification of significant events and high-risk Incidents (72 hours) Jordan: Central Bank of Jordan Instructions of Cyber Risks Resilience, Notification of Cyber Events to the Central Bank (72 hours) Andorra: Llei 22/2022, Incident Handling and Notification Obligation (72 hours) Antigua and Barbuda: Antigua and Barbuda Eastern Caribbean Central Bank Electronic Banking Standard, Incident Reporting (3 days) Antigua and Barbuda: Antigua and Barbuda Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (72 hours) Albania: AKEP Regulation On Organisational and Technical Security Measures, Incident Reporting (72 hours) Albania: Law On Cybersecurity, Incident Reporting by Operators of Critical and Important Information Infrastructure (72 hours) Armenia: Law on Cybersecurity: Cyber Incident Notification (72 hours) Bermuda: Bermuda Monetary Authority Insurance Sector Operational Cyber Risk Management Code of Conduct, Notification of Cyber Reporting Events (72 hours) Bermuda: Bermuda Monetary Authority Operational Cyber Risk Management Code of Conduct, Notification of Cyber Reporting Events (72 hours) Micronesia: FSM Cybersecurity Act 2025 (Bill), Critical Information Infrastructure Incident Reporting Clock (72 hours) Grenada: Grenada ECCB Electronic Banking Standard, Incident Reports to the Central Bank Within Three Days (3 days) Grenada: Grenada ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (72 hours) Saint Kitts and Nevis: Saint Kitts and Nevis Eastern Caribbean Central Bank Electronic Banking Standard, Incident Reporting (3 days) Saint Kitts and Nevis: Saint Kitts and Nevis Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (72 hours) Cayman Islands: CIMA Rule on Cybersecurity for Regulated Entities, Notification Requirements (72 hours) Saint Lucia: Saint Lucia ECCB Electronic Banking Standard, Incident Reports to the Central Bank Within Three Days (3 days) Saint Lucia: Saint Lucia ECCB Technology Risk Management Standard, Cyber-Incident Alert, Report and Customer Notice (72 hours) Liechtenstein: Cyber-Sicherheitsgesetz (CSG), Incident Notification (72 hours) Moldova: Law 48/2023 on Cybersecurity: Cyber Incident Notification (72 hours) Montenegro: Law on Information Security, Cyber Threat and Incident Reporting (72 hours) Marshall Islands: Cybersecurity Act 2025, Cybersecurity Incident Reporting Obligations (72 hours) North Macedonia: Law on Security of Network and Information Systems, Significant Incident and Threat Notification (72 hours) Norway: Incident Notification by Providers of Essential Societal Services and Digital Services (72 hours) Serbia: Law on Information Security, Incident Reporting Obligations (3 days) Vatican City: Payment Services Major Incident Notification (3 business days) Saint Vincent and the Grenadines: Saint Vincent and the Grenadines Eastern Caribbean Central Bank Electronic Banking Standard, Incident Reporting (3 days) Saint Vincent and the Grenadines: Saint Vincent and the Grenadines Eastern Caribbean Central Bank Technology Risk Management Standard, Cyber-Incident Reporting (72 hours) Kosovo: Central Bank Regulation on Information Systems and Cyber Risk Management, Incident Reporting (72 hours) Australia: Security of Critical Infrastructure Act, Notification of Cyber Security Incidents (84 hours) United States: SEC Cybersecurity Risk Management, Governance, and Incident Disclosure (Regulation S-K Item 106; Form 8-K Item 1.05) (4 business days) Missouri: Insurance Data Security Act: notice of a cybersecurity event to the director (4 business days) Latvia: Nacionālās kiberdrošības likums, Coordinated Vulnerability Disclosure and Remediation (5 business days) United States: SEC Regulation SCI: notification of SCI events to the Commission and to members (5 business days) Arkansas: Public entity security incident report to the Legislative Auditor (5 business days) Minnesota: Minnesota Insurance Data Security Act, notification of a cybersecurity event to the commissioner (5 business days) Tennessee: State agency notice to the Comptroller of the Treasury of unauthorized data acquisition or a security system breach (5 business days) Utah: Government Data Privacy Act, notification of a data breach by a governmental entity to the Utah Cyber Center (5 days) Brunei Darussalam: BDCB Notice on Cyber Intrusion and IT Incident Reporting by Banks (5 business days) Indonesia: OJK Regulation on Information Technology in Commercial Banks, Reporting of IT and Cyber Incidents (5 business days) Vietnam: Circular on Information System Security in Banking Operations, Incident Reporting to the State Bank (5 business days) Argentina: BCRA Cyber-Incident Notification (Guidelines for Response and Recovery from Cyber-Incidents) (5 days) Brazil: SUSEP Circular 638 of 2021, Notification of Relevant Incidents (5 business days) Costa Rica: General Regulation on Information Technology Governance and Management (CONASSIF Agreement 5-24), Incident Classification and Reporting (5 business days) Honduras: CNBS Norms on Information Technology, Information Security and Cybersecurity Management (Circular CNBS 025/2022), Incident Notification (5 business days) Kenya: Virtual Asset Service Providers Regulations, Reporting of Cybersecurity Incidents (5 business days) Seychelles: Seychelles Virtual Asset Service Providers (Cyber Security Requirements) Regulations, 2024: Reporting of Cyber Security Risk (5 business days) Azerbaijan: Rules on Information Security Management in Banks, High-Category Incident Report to the Central Bank (5 business days) Croatia: Zakon o kibernetičkoj sigurnosti and Uredba o kibernetičkoj sigurnosti, Incident and Cyber-Threat Reporting Obligations (7 days) Portugal: Regime Jurídico da Cibersegurança, Significant-Incident Reporting Obligations (1 week) Florida: Local Government Cybersecurity Act, cybersecurity incident and ransomware reporting (1 week) Florida: State Cybersecurity Act, state agency cybersecurity incident and ransomware reporting (1 week) Ohio: Political Subdivision Cybersecurity, incident notice to homeland security and the auditor of state (7 days) Papua New Guinea: Cybersecurity Bill 2026, Incident Reporting by CII Operators and Financial Institutions (7 days) Chile: Cybersecurity Incident Reporting Regulation under the Ley Marco de Ciberseguridad (7 days) Chile: Ley Marco de Ciberseguridad, Reporting of Cybersecurity Incidents (7 days) El Salvador: Technical Standards for Information Security Management (NRP-23), Incident Communication (7 business days) Trinidad and Tobago: Virtual Assets and Virtual Asset Service Providers Act, Notice of a Cyber-Security Event by a Sandbox Participant (7 business days) Kenya: Virtual Asset Service Providers Act, Notice of a Cyber-Security Incident (7 business days) Nigeria: NCC Cyber Resilience Framework for the Nigerian Communication Sector, Cyber Incident Reporting to NCC-CSIRT (7 days) Sierra Leone: Cyber Security and Crime Act, 2021, Reporting of Cyber Security Incidents (7 days) Bahrain: Cyber Security Incident Reporting for Conventional Bank Licensees (Rulebook Volume 1, Module OM, Section OM-5.5) (1 week) Bahrain: Cyber Security Incident Reporting for Crypto-Asset Licensees (Rulebook Volume 6, Module CRA, Section CRA-5.8) (1 week) Bahrain: Cyber Security Incident Reporting for Insurance Licensees (Rulebook Volume 3, Module RM, Section RM-9.1) (1 week) Bahrain: Cyber Security Incident Reporting for Investment Business Licensees (Rulebook Volume 4, Module RM, Section RM-9.1) (1 week) Bahrain: Cyber Security Incident Reporting for Islamic Bank Licensees (Rulebook Volume 2, Module OM, Section OM-5.5) (1 week) Michigan: Michigan Insurance Data Security Act, cybersecurity event investigation and notice to the director (10 business days) New Mexico: Cybersecurity incident reporting order for agencies and political subdivisions (10 days) West Virginia: State agencies, local governments and other public bodies, cyber incident reporting to the Cybersecurity Office (10 days) Australia: Prudential Standard CPS 234 Information Security, Notification to APRA (10 business days) China: People's Bank of China Cybersecurity Incident Reporting Measures, financial institution duties (10 business days) Trinidad and Tobago: Virtual Assets and Virtual Asset Service Providers Act, Notice of a Cyber-Security Event by a Sandbox Participant (10 days) Bahrain: Cyber Security Incident Reporting for Conventional Bank Licensees (Rulebook Volume 1, Module OM, Section OM-5.5) (10 days) Bahrain: Cyber Security Incident Reporting for Crypto-Asset Licensees (Rulebook Volume 6, Module CRA, Section CRA-5.8) (10 days) Bahrain: Cyber Security Incident Reporting for Insurance Licensees (Rulebook Volume 3, Module RM, Section RM-9.1) (10 days) Bahrain: Cyber Security Incident Reporting for Investment Business Licensees (Rulebook Volume 4, Module RM, Section RM-9.1) (10 days) Bahrain: Cyber Security Incident Reporting for Islamic Bank Licensees (Rulebook Volume 2, Module OM, Section OM-5.5) (10 days) European Union: Cyber Resilience Act, Manufacturer Reporting Obligations (14 days) Hong Kong: Protection of Critical Infrastructures (Computer Systems) Ordinance, Incident Notification (14 days) Sri Lanka: Reporting of Information Technology and Cybersecurity Incidents of Licensed Banks (14 days) Singapore: MAS Notice FSM-N05, Report of Relevant Incidents by Banks (14 days) Antigua and Barbuda: Antigua and Barbuda Digital Assets Business Act 2020, Compliance Officer Report of a Cyber Reporting Event (14 days) Bermuda: Bermuda Digital Asset Business Act 2018: Senior Representative's Notice and Report of a Cyber Reporting Event (14 days) Bermuda: Bermuda Monetary Authority Insurance Sector Operational Cyber Risk Management Code of Conduct, Notification of Cyber Reporting Events (14 days) Bermuda: Bermuda Monetary Authority Operational Cyber Risk Management Code of Conduct, Notification of Cyber Reporting Events (14 days) Switzerland: Mandatory Reporting of Cyberattacks on Critical Infrastructure (14 days) Vatican City: Payment Services Major Incident Notification (2 weeks) Cyprus: Security of Networks and Information Systems Law, Incident Notification Obligations (15 days) Texas: Texas money services business regulation, notice of a cybersecurity incident to the banking commissioner (15 days) Texas: Texas trust company regulation, notice of a cybersecurity incident to the banking commissioner (15 days) Chile: Cybersecurity Incident Reporting Regulation under the Ley Marco de Ciberseguridad (15 days) Chile: Ley Marco de Ciberseguridad, Reporting of Cybersecurity Incidents (15 days) Honduras: CNBS Norms on Information Technology, Information Security and Cybersecurity Management (Circular CNBS 025/2022), Incident Notification (15 business days) Serbia: Law on Information Security, Incident Reporting Obligations (15 days) Spain: Real Decreto-ley 12/2018, Incident Notification Obligation (20 days) Barbados: Technology and Cyber Risk Management Guideline, Reporting of Cyber Incidents to the Financial Services Commission (20 business days) European Union: Cyber Resilience Act, Manufacturer Reporting Obligations (1 month) European Union: DORA, Article 19 (reporting of major ICT-related incidents), with the time limits of Delegated Regulation (EU) 2025/301 (1 month) European Union: NIS2 Directive, Reporting Obligations (1 month) Austria: Netz- und Informationssystemsicherheitsgesetz 2026 (NISG 2026), Significant-Incident Reporting Obligations (1 month) Belgium: Loi du 26 avril 2024, Significant-Incident Notification Obligations (1 month) Bulgaria: Cybersecurity Act, Incident and Cyber-Threat Reporting Obligations (Zakon za kibersigurnost, ZKS) (1 month) Cyprus: Security of Networks and Information Systems Law, Incident Notification Obligations (1 month) Czech Republic: Cybersecurity Act (Zákon o kybernetické bezpečnosti), Incident Notification (30 days) Germany: BSI-Gesetz (BSIG), Incident Notification (1 month) Denmark: Act on Security and Preparedness in the Telecoms Sector (Lov om sikkerhed og beredskab i telesektoren), Significant Incident Notification (1 month) Denmark: NIS 2-loven, Significant-Incident Reporting and Recipient-Notice Duties (1 month) Estonia: Küberturvalisuse seadus (KüTS), Duty to Notify of a Cyber Incident (1 month) Spain: Anteproyecto de Ley de Coordinación y Gobernanza de la Ciberseguridad, Incident Reporting Obligations (1 month) Finland: Kyberturvallisuuslaki, Significant-Incident Reporting Obligations (1 month) France: Projet de loi Résilience des Infrastructures Critiques et Cybersécurité, Incident Notification (NIS2) (1 month) Greece: Law 5160/2024, Significant-Incident Reporting Obligations (1 month) Croatia: Zakon o kibernetičkoj sigurnosti and Uredba o kibernetičkoj sigurnosti, Incident and Cyber-Threat Reporting Obligations (30 days) Hungary: Cybersecurity Act, Incident Notification and Cybersecurity Fine (1 month) Ireland: National Cyber Security Bill, Incident Response Powers and Reporting Obligations (1 month) Italy: Decreto Legislativo 4 settembre 2024, n. 138 (Decreto NIS2), Incident Notification (1 month) Lithuania: Kibernetinio saugumo įstatymas (Law on Cyber Security), Incident Notification (1 month) Luxembourg: Loi du 5 mai 2026 relative à la cybersécurité (NIS2), Incident Notification (1 month) Latvia: Nacionālās kiberdrošības likums, Incident Notification (1 month) Malta: Measures for a High Common Level of Cybersecurity across the European Union (Malta) Order, Significant-Incident Reporting to the National CSIRT (1 month) Netherlands: Cyberbeveiligingswet, Significant-Incident Reporting Obligations (1 month) Poland: Ustawa o krajowym systemie cyberbezpieczeństwa (KSC), Zgłaszanie Incydentów Poważnych (1 month) Portugal: Regime Jurídico da Cibersegurança, Significant-Incident Reporting Obligations (30 business days) Romania: Ordonanța de urgență nr. 155/2024, Incident Notification (1 month) Sweden: Cybersäkerhetslag, Incident Notification (1 month) Slovenia: Zakon o informacijski varnosti (ZInfV-1), Significant-Incident Notification Obligations (1 month) Slovakia: Zákon o kybernetickej bezpečnosti (Cybersecurity Act), Incident and Vulnerability Notification (1 month) United States: SEC Regulation SCI: notification of SCI events to the Commission and to members (30 days) New York: Cybersecurity incident reporting by municipal corporations and public authorities (30 days) New York: New York Department of Financial Services Cybersecurity Regulation, Notices to the Superintendent (30 days) Ohio: Political Subdivision Cybersecurity, incident notice to homeland security and the auditor of state (30 days) Puerto Rico: Government Cybersecurity Act, incident reporting to the Puerto Rico Innovation and Technology Service (1 month) China: National Cybersecurity Incident Reporting Measures (30 days) Japan: Important Computers Act, Report of Specified Infringement Events (30 days) Mongolia: Law on Cyber Security, Critical Information Infrastructure Organizations' Duty to Notify Cyber-Attacks and Failures (1 month) Singapore: Cybersecurity Act 2018, Report of Cybersecurity Incidents on Provider-Owned Critical Information Infrastructure (30 days) Taiwan: Cyber Security Incident Reporting, Response and Drills Regulations, Specific Non-Government Agency Clocks (1 month) Ghana: Bank of Ghana Cyber and Information Security Directive, Incident Reporting (1 month) Liberia: Central Bank of Liberia Mobile Money Regulations, 2014: Reporting of Security Breaches and Service Interruptions (1 month) Mozambique: Cybersecurity Law, Incident Notification and Responsible Vulnerability Disclosure (1 month) Namibia: Bank of Namibia Determination of the Operational and Cybersecurity Standards within the National Payment System (PSD-12), Cyber Incident Reporting (1 month) Seychelles: Seychelles National Payment System (Electronic Money) Regulations, 2022: Reporting of Security Breaches and Loss of Confidential Data (1 month) Andorra: Llei 22/2022, Incident Handling and Notification Obligation (1 month) Albania: AKEP Regulation On Organisational and Technical Security Measures, Incident Reporting (30 days) Albania: Law On Cybersecurity, Incident Reporting by Operators of Critical and Important Information Infrastructure (1 month) Armenia: Law on Cybersecurity: Cyber Incident Notification (1 month) Micronesia: FSM Cybersecurity Act 2025 (Bill), Critical Information Infrastructure Incident Reporting Clock (30 days) Liechtenstein: Cyber-Sicherheitsgesetz (CSG), Incident Notification (1 month) Moldova: Law 48/2023 on Cybersecurity: Cyber Incident Notification (1 month) Montenegro: Law on Information Security, Cyber Threat and Incident Reporting (1 month) Marshall Islands: Cybersecurity Act 2025, Cybersecurity Incident Reporting Obligations (30 days) North Macedonia: Law on Security of Network and Information Systems, Significant Incident and Threat Notification (1 month) Norway: Incident Notification by Providers of Essential Societal Services and Digital Services (1 month) Kosovo: Central Bank Regulation on Information Systems and Cyber Risk Management, Incident Reporting (30 days) Spain: Real Decreto-ley 12/2018, Incident Notification Obligation (40 days) China: People's Bank of China Cybersecurity Incident Reporting Measures, financial institution duties (40 business days) Israel: Directive 366, reporting of technological failures, data security incidents and cyber attacks (45 days) Argentina: BCRA Cyber-Incident Notification (Guidelines for Response and Recovery from Cyber-Incidents) (60 business days) Israel: Directive 366, reporting of technological failures, data security incidents and cyber attacks (60 days) 16 19 15 109 25 113 16 18 11 10 58 Privacy law European Union: Commission Regulation on Personal Data Breach Notification by Electronic Communications Providers (Regulation (EU) No 611/2013) (24 hours) Georgia: Georgia Personal Identity Protection Act, notification of security breach (24 hours) Idaho: Identity Theft Act, breach of security disclosure duty (24 hours) Indonesia: Implementing Regulation on Personal Data Protection, breach notification (24 hours) Kazakhstan: Law on Personal Data and Their Protection, breach notification (1 business day) Zambia: Data Protection Act, 2021, notification of a security breach (24 hours) Zimbabwe: Cyber and Data Protection Act, security breach notification (24 hours) Zimbabwe: Cyber and Data Protection Regulations 2024, security breach notification (24 hours) Jordan: Personal Data Protection Law, breach notification (24 hours) Kuwait: CITRA Data Privacy Protection Regulation, personal data breach notification (24 hours) Russia: Federal Law No. 152-FZ, Article 21 Part 3.1, Breach Notification (24 hours) Minnesota: Minnesota breach notification (48 hours) Ecuador: LOPDP, notificación de vulneración de seguridad (2 days) Peru: Reglamento de la Ley 29733 (Decreto Supremo 016-2024-JUS), security incidents and access records (48 hours) Burundi: Law No. 1/03 of March 10, 2026 on the Protection of Personal Data, personal data breach notification (48 hours) Kenya: Data Protection Act, 2019, personal data breach notification (48 hours) Nigeria: Internet Code of Practice 2026, data breach notification (48 hours) Rwanda: Law relating to the Protection of Personal Data and Privacy, personal data breach notification (48 hours) Belize: Data Protection Act 2021, personal data breach notification (70 hours) European Union: Commission Regulation on Personal Data Breach Notification by Electronic Communications Providers (Regulation (EU) No 611/2013) (3 days) European Union: GDPR Articles 33-34, Breach Notification (72 hours) Austria: GDPR Articles 33-34, Breach Notification in Austria (72 hours) Belgium: GDPR Articles 33-34, Breach Notification (72 hours) Bulgaria: Electronic Communications Act Articles 261в to 261д, Personal Data Breach Notification by Providers of Public Electronic Communications Services (3 days) Bulgaria: GDPR Articles 33-34, Breach Notification (72 hours) Cyprus: GDPR Articles 33-34 and Law 125(I)/2018 Article 12, Breach Notification in Cyprus (72 hours) Czech Republic: GDPR Articles 33-34, Breach Notification (72 hours) Germany: GDPR Articles 33-34, Breach Notification in Germany (72 hours) Denmark: GDPR Articles 33-34, Breach Notification in Denmark (72 hours) Estonia: GDPR Articles 33-34, Breach Notification in Estonia (72 hours) Spain: GDPR Articles 33-34 and LOPDGDD Articles 73(r)-(s) and 74(m)-(n), Breach Notification (72 hours) Finland: GDPR Articles 33-34, Breach Notification in Finland (72 hours) France: GDPR Articles 33-34, Breach Notification (72 hours) Greece: GDPR Articles 33-34, Breach Notification in Greece (72 hours) Croatia: GDPR Articles 33-34, Breach Notification (72 hours) Hungary: GDPR Articles 33-34 and Infotörvény Sections 25/J-25/K, Breach Notification in Hungary (72 hours) Ireland: GDPR Articles 33-34, Breach Notification in Ireland (72 hours) Italy: GDPR Articles 33-34, Breach Notification (72 hours) Lithuania: GDPR Articles 33-34, Breach Notification in Lithuania (72 hours) Luxembourg: GDPR Articles 33-34, Breach Notification in Luxembourg (72 hours) Latvia: GDPR Articles 33-34, Breach Notification in Latvia (72 hours) Malta: GDPR Articles 33-34, Breach Notification in Malta (72 hours) Netherlands: GDPR Articles 33-34 and UAVG Article 42, Breach Notification (72 hours) Poland: GDPR Articles 33-34, Breach Notification (72 hours) Portugal: GDPR Articles 33-34, Breach Notification in Portugal (72 hours) Romania: GDPR Articles 33-34, Breach Notification (72 hours) Sweden: GDPR Articles 33-34, Breach Notification (72 hours) Slovenia: GDPR Articles 33-34, Breach Notification (72 hours) Slovakia: GDPR Articles 33-34, Breach Notification (72 hours) United Kingdom: UK GDPR Articles 33-34 and PECR, Breach Notification in the United Kingdom (72 hours) United States: Regulation S-P: incident response program and customer breach notice (72 hours) Alabama: Insurance Data Security Law: notice of a cybersecurity event to the Commissioner of Insurance (3 business days) Connecticut: Insurance Data Security Law: notice of a cybersecurity event to the Insurance Commissioner (3 business days) Delaware: Insurance Data Security Act: notification of a cybersecurity event (3 business days) Iowa: Insurance Data Security Act: notice of a cybersecurity event to the Commissioner of Insurance (3 business days) Illinois: Personal Information Protection Act, data breach notification (72 hours) Indiana: Insurance Data Security: notice of a cybersecurity event to the insurance commissioner (3 business days) Kentucky: Insurance Data Security Law: licensee notice of a cybersecurity event to the Commissioner of Insurance (3 business days) Louisiana: Insurance Data Security Law: notification of a cybersecurity event to the commissioner of insurance (3 business days) Maryland: Insurance Data Security Act: investigation of a cybersecurity event and notice to the Insurance Commissioner (3 business days) Minnesota: Insurance data security law: notification of a cybersecurity event to the commissioner and to consumers (3 business days) New Hampshire: Insurance Data Security Law: licensee notice of a cybersecurity event to the insurance commissioner (3 business days) Oklahoma: Insurance Data Security Act: notification of a cybersecurity event to the Insurance Commissioner (3 business days) Pennsylvania: Breach of Personal Information Notification Act (3 business days) Pennsylvania: Insurance Data Security: notification of a cybersecurity event to the Insurance Commissioner (3 business days) Rhode Island: Insurance Data Security: notice of a cybersecurity event to the Commissioner by a domestic insurer (3 business days) Rhode Island: Insurance Data Security: notice of a cybersecurity event to the Commissioner by an insurer affecting 250 or more Rhode Island consumers (3 business days) Tennessee: Insurance Data Security Law: notification of a cybersecurity event to the commissioner, consumers and producers of record (3 business days) Virginia: Insurance Data Security Act: notice of a cybersecurity event to the Commissioner and to consumers (3 business days) Brunei Darussalam: Personal Data Protection Order 2025, breach notification (3 days) Indonesia: Implementing Regulation on Personal Data Protection, breach notification (72 hours) Indonesia: Law on Personal Data Protection, breach notification (72 hours) India: Digital Personal Data Protection Act, 2023, breach notification duties (72 hours) Cambodia: Cambodia's Draft Law on Personal Data Protection, personal data breach notification (72 hours) South Korea: Personal Information Protection Act, breach notification duties (72 hours) Malaysia: Personal Data Protection Act, data protection officer and breach notification (72 hours) Singapore: Personal Data Protection Act, data breach notification (3 days) Thailand: Personal Data Protection Act, breach notification (72 hours) Vietnam: Law on Personal Data Protection, breach notification (72 hours) Barbados: Data Protection Act, 2019, personal data breach notification (72 hours) Brazil: ANPD Regulation on Reporting Security Incidents (Resolution CD/ANPD No. 15/2024) (3 business days) Bahamas: Data Protection Act, 2025, personal data breach notification (72 hours) Belize: Data Protection Act 2021, personal data breach notification (72 hours) Ecuador: LOPDP, notificación de vulneración de seguridad (3 days) Guyana: Data Protection Act 2023, personal data breach notification (72 hours) Jamaica: Data Protection Act, 2020, reporting a contravention or security breach (72 hours) Paraguay: Ley N° 7593/2025, notificación de un incidente de seguridad (72 hours) Suriname: Draft Law on the Protection of Privacy and Personal Data, breach notification (72 hours) El Salvador: Ley para la Protección de Datos Personales, personal data breach notification (72 hours) Uruguay: Decreto N° 64/020, personal data breach communication (72 hours) Botswana: Data Protection Act, 2024, personal data breach notification (72 hours) Republic of the Congo: Law No. 29-2019, personal-data breach notification (72 hours) Cabo Verde: Law No. 133/V/2001 on the Protection of Personal Data, personal data breach notification (72 hours) Djibouti: Digital Code, Book I: personal-data breach notification (72 hours) Egypt: Egypt Personal Data Protection Law, Personal Data Infringement notification (72 hours) Ethiopia: Personal Data Protection Proclamation, personal data breach notification (72 hours) Gambia: Personal Data Protection and Privacy Act, 2025, personal data breach notification (72 hours) Kenya: Data Protection Act, 2019, personal data breach notification (72 hours) Mauritius: Data Protection Act 2017, personal data breach notification (72 hours) Niger: Loi n° 2022-59, notification des violations de données (72 hours) Nigeria: Nigeria Data Protection Act, 2023, data breach notification (72 hours) Rwanda: Law relating to the Protection of Personal Data and Privacy, personal data breach notification (72 hours) Seychelles: Data Protection Act, 2023, personal data breach notification (72 hours) Somalia: Data Protection Act, 2023, personal data breach notification (72 hours) Zimbabwe: Cyber and Data Protection Regulations 2024, security breach notification (72 hours) United Arab Emirates: ADGM Data Protection Regulations, breach notification (72 hours) Jordan: Personal Data Protection Law, breach notification (72 hours) Kuwait: CITRA Data Privacy Protection Regulation, personal data breach notification (72 hours) Oman: Personal Data Protection Law, breach notification (72 hours) Qatar: Personal Data Privacy Protection Law, breach notification (72 hours) Qatar: QFC Data Protection Regulations 2021, breach notification (72 hours) Saudi Arabia: Personal Data Protection Law, breach notification (72 hours) Syria: Law No. 12 of 2024 on Protection of Electronic Personal Data, personal data breach notification (72 hours) Andorra: LQPD, personal data breach notification (72 hours) Albania: Law No. 124/2024, notification of a personal data breach (72 hours) Bosnia and Herzegovina: Law on the Protection of Personal Data of Bosnia and Herzegovina, personal data breach notification (72 hours) Belarus: Law of the Republic of Belarus On Personal Data Protection, notification of personal data protection violations (3 business days) Georgia: Law on Personal Data Protection, breach notification (72 hours) Iceland: Act No. 90/2018, Breach Notification in Iceland (72 hours) Liechtenstein: DSG Breach Notification in Liechtenstein (72 hours) Monaco: Loi sur la Protection des Données Personnelles, notification des violations de données (72 hours) Moldova: Moldova Law No. 195/2024, personal data breach notification (72 hours) North Macedonia: Law on Personal Data Protection (LPDP), personal data breach notification (72 hours) Maldives: Maldives Personal Data Protection Bill, personal data breach notification (72 hours) Norway: Personal Data Act, Breach Notification in Norway (72 hours) Serbia: Law on Personal Data Protection, personal data breach notification (72 hours) Russia: Federal Law No. 152-FZ, Article 21 Part 3.1, Breach Notification (72 hours) San Marino: San Marino Law No. 171, personal data breach notification (72 hours) Tonga: Privacy Act 2025, personal information breaches (72 hours) Turkey: Personal Data Protection Law (KVKK), breach notification (72 hours) Ukraine: Draft Law No. 8153, personal data breach notification (72 hours) Vatican City: General Regulation on the Protection of Personal Data, reporting of personal data violations (72 hours) Samoa: National Digital Identification Act 2024, personal data breach notification (72 hours) Kosovo: Law No. 06/L-082 on Protection of Personal Data, personal data breach notification (72 hours) Burundi: Law No. 1/03 of March 10, 2026 on the Protection of Personal Data, personal data breach notification (96 hours) Iowa: Personal Information Security Breach Protection (5 business days) Illinois: Personal Information Protection Act, data breach notification (5 business days) Minnesota: Insurance data security law: notification of a cybersecurity event to the commissioner and to consumers (5 business days) New York: Stop Hacks and Improve Electronic Data Security (SHIELD) Act, breach notification duty (5 business days) Pennsylvania: Insurance Data Security: notification of a cybersecurity event to the Insurance Commissioner (5 business days) Ecuador: LOPDP, notificación de vulneración de seguridad (5 days) Algeria: Loi n° 18-07 relative à la protection des personnes physiques, notification des violations de données (5 days) Cayman Islands: Data Protection Act 2021 Revision, personal data breach notification (5 days) United States: FCC CPNI breach notification rule (7 business days) Maryland: Maryland Personal Information Protection Act (MPIPA), breach notification (7 days) Maine: Notice of Risk to Personal Data (7 business days) Pennsylvania: Breach of Personal Information Notification Act (7 business days) Bahamas: Data Protection Act, 2025, personal data breach notification (7 business days) Alabama: Alabama Data Breach Notification Act of 2018 (10 days) Florida: Florida Information Protection Act, breach notification (10 days) Maryland: Maryland Personal Information Protection Act (MPIPA), breach notification (10 days) New York: Stop Hacks and Improve Electronic Data Security (SHIELD) Act, breach notification duty (10 days) Oregon: Notice of breach of security (10 days) Puerto Rico: Ley de Información al Ciudadano sobre la Seguridad de Bancos de Información (data breach notification) (10 days) Vermont: Data Broker Security Breach Notice Act: notice to consumers and the Attorney General (14 business days) Vermont: Security Breach Notice Act (14 business days) Nigeria: Internet Code of Practice 2026, data breach notification (14 days) California: California Data Breach Notification Law, as amended by SB 446 (15 days) California: Health facility medical information breach reporting (15 business days) Zimbabwe: Cyber and Data Protection Regulations 2024, security breach notification (21 days) United States: FCC CPNI breach notification rule (30 days) United States: GLBA Safeguards Rule Breach Notification Amendment (30 days) United States: Regulation S-P: incident response program and customer breach notice (30 days) California: California Data Breach Notification Law, as amended by SB 446 (30 days) California: Health facility medical information breach reporting (30 days) Colorado: C.R.S. 6-1-716, Notification of Security Breach (30 days) Florida: Florida Information Protection Act, breach notification (30 days) Maine: Notice of Risk to Personal Data (30 days) New York: Stop Hacks and Improve Electronic Data Security (SHIELD) Act, breach notification duty (30 days) Rhode Island: Identity Theft Protection Act of 2015, notification of breach (30 days) Texas: Identity Theft Enforcement and Protection Act, breach notification (30 days) Washington: Notice of security breaches involving personal information (30 days) Ontario: Personal Health Information Protection Act, 2004, breach notification by custodians and agents (30 days) Alabama: Alabama Data Breach Notification Act of 2018 (45 days) Arkansas: Arkansas Personal Information Protection Act, breach notification and security (45 days) Arizona: Arizona data breach notification law (45 days) Illinois: Personal Information Protection Act, data breach notification (45 days) Indiana: Disclosure of Security Breach Act (45 days) Maryland: Maryland Personal Information Protection Act (MPIPA), breach notification (45 days) New Mexico: Data Breach Notification Act (45 days) Ohio: Security Breach Notification Act (45 days) Oregon: Notice of breach of security (45 days) Rhode Island: Identity Theft Protection Act of 2015, notification of breach (45 days) Tennessee: Insurance Data Security Law: notification of a cybersecurity event to the commissioner, consumers and producers of record (45 days) Vermont: Data Broker Security Breach Notice Act: notice to consumers and the Attorney General (45 days) Vermont: Security Breach Notice Act (45 days) Wisconsin: Notice of unauthorized acquisition of personal information (45 days) United States: FTC Health Breach Notification Rule (60 days) United States: HIPAA Breach Notification Rule (60 days) California: Health facility medical information breach reporting (60 days) Connecticut: Breach of security re computerized data containing personal information (60 days) Delaware: Computer Security Breaches (60 days) Delaware: Insurance Data Security Act: notification of a cybersecurity event (60 days) Louisiana: Database Security Breach Notification Law, notice duty (60 days) Oklahoma: Security Breach Notification Act (60 days) South Dakota: Breach of system security, notification statute (60 days) Texas: Identity Theft Enforcement and Protection Act, breach notification (60 days) 11 115 13 14 10 AI law, high-risk systems Malta: Artificial Intelligence (Designation of the Information and Data Protection Commissioner for the purposes of Regulation (EU) 2024/1689) Regulations, 2025 (L.N. 227 of 2025) (24 hours) European Union: AI Act, Article 26(10) (post-remote biometric identification authorisation) (48 hours) European Union: AI Act, Article 73 (reporting of serious incidents) (2 days) European Union: AI Act, Articles 60 and 61 (testing in real world conditions outside AI regulatory sandboxes, with informed consent) (2 days) Italy: Decreto Legislativo 160/2026, After-the-Fact Facial Recognition Integrated in Video Surveillance (Art. 10) (48 hours) Malta: Artificial Intelligence (Designation of the Information and Data Protection Commissioner for the purposes of Regulation (EU) 2024/1689) Regulations, 2025 (L.N. 227 of 2025) (48 hours) New Jersey: AI-based electronic monitoring and automated employment decision systems in employment and public services (S4075 / A4981) (48 hours) Vietnam: Decree implementing the AI Law, serious incident reporting and handling (72 hours) Vietnam: Law on Artificial Intelligence, incident management and reporting obligation (72 hours) Chile: Boletín 16.821-19, obligaciones para sistemas de IA de alto riesgo (72 hours) Vietnam: Decree implementing the AI Law, serious incident reporting and handling (5 business days) Vietnam: Law on Artificial Intelligence, incident management and reporting obligation (5 business days) European Union: AI Act, Article 73 (reporting of serious incidents) (10 days) European Union: AI Act, Articles 60 and 61 (testing in real world conditions outside AI regulatory sandboxes, with informed consent) (10 days) New York: New York Artificial Intelligence Act (10 days) European Union: AI Act, Article 73 (reporting of serious incidents) (15 days) European Union: AI Act, Articles 60 and 61 (testing in real world conditions outside AI regulatory sandboxes, with informed consent) (15 days) Vietnam: Decree implementing the AI Law, risk classification, notification, conformity assessment and risk management (15 business days) Vietnam: Decree implementing the AI Law, serious incident reporting and handling (15 days) New Jersey: AI-based electronic monitoring and automated employment decision systems in employment and public services (S4075 / A4981) (30 days) New Jersey: AI-based electronic monitoring and automated employment decision systems in employment and public services (S4075 / A4981) (60 days) AI law, frontier models California: Transparency in Frontier Artificial Intelligence Act (SB 53) (24 hours) Illinois: Artificial Intelligence Safety Measures Act (24 hours) Massachusetts: Transparency in Frontier Artificial Intelligence Act (proposed chapter 93M, Senate version of House bill 5576) (24 hours) New York: Responsible AI Safety and Education Act (RAISE Act) (24 hours) Pennsylvania: H.B. 2800, Artificial Intelligence Risk Prevention Act (24 hours) Pennsylvania: H.B. 2829, Frontier Artificial Intelligence Safety, Transparency and Accountability Act (24 hours) United States: Artificial Intelligence Risk Management and Security Act of 2026 (72 hours) Illinois: Artificial Intelligence Safety Measures Act (72 hours) New York: Responsible AI Safety and Education Act (RAISE Act) (72 hours) Pennsylvania: H.B. 2800, Artificial Intelligence Risk Prevention Act (72 hours) Pennsylvania: H.B. 2829, Frontier Artificial Intelligence Safety, Transparency and Accountability Act (72 hours) California: Transparency in Frontier Artificial Intelligence Act (SB 53) (15 days) Massachusetts: Transparency in Frontier Artificial Intelligence Act (proposed chapter 93M, Senate version of House bill 5576) (15 days) United States: Artificial Intelligence Risk Management and Security Act of 2026 (30 days) 1 h 6 h 24 h 72 h 7 d 14 d 30 d 90 d 72 hours 4 business days 14 days 30 days 90 days
Each flag is one law, and a link to it. A keyhole into the drawing, from 12 hours to 12 days.

See every clock, and the sentence that sets it

The law library today

272jurisdictions tracked
5,430provisions on file
2,406stories on file

LexLint checks AI, scraping, privacy, cybersecurity, communications, content-moderation, product-liability, digital-accessibility, digital-identity, cloud-service, export-control, age-gating and reuse law. The jurisdiction and provision counts above cover the areas the law library lists, recounted at each build. The law library is rebuilt and republished daily; the research runs in waves, every provision carries the date it was last read against its source. How current is this

Your code and data are not visible to us.
The declaration is the whole request. A run reaches the portal only if you choose to upload it. What is sent, and what never is
The same deal your linter makes.
Early warning on the basics, cited to the instrument, with a note for counsel where judgment is needed. Nobody mistakes a clean lint for a QA sign-off, and a clean run never says "compliant". What it is, and what it is not
Built on public law, in the open.
Every finding cites its source and links the law note behind it where we keep one, and every note says when it was last checked against its source. The law library

Powered by
UnGovr is a nonprofit transparency platform. It builds and runs LexLint, and the LexLint law library is what the lint reads. About UnGovr →

UnGovr is an Associate Member of
Agentic AI Foundation, Associate Member The Linux Foundation, Associate Member Open Secure AI Alliance, Associate Member

The Agentic AI Foundation is the Linux Foundation initiative behind the Model Context Protocol, the standard LexLint speaks. The Open Secure AI Alliance is the Linux Foundation fund on the security of AI agents and the systems they reach. The memberships are UnGovr's own: none of the three reviews, certifies, or endorses LexLint or its findings.

UnGovr is a licensed Supporter of
CIS Critical Security Controls Supporter, read the CIS Controls against the law

CIS licenses us to show its Controls' Safeguard numbers beside the laws they bear on. The summaries and the mapping are our own; CIS has not reviewed or endorsed them. The CIS Controls, read against the law →