LexLint for technical teams

One run, read four ways.

One run, read four ways One run in the middle, read by four people: the developer, who fixes the work items; the product owner, who sees readiness by place; the security, who reads the security findings; the platform, who wires it into the pipeline. Technical teams One run, read four ways One run </> Developer fixes the work items Product owner sees readiness by place Security reads the security findings Platform wires it into the pipeline

Four roles

  • Developer

    Findings in the coding CLI you already use, fixed while the code is fresh.

    Install LexLint
  • Product owner

    Where the app stands in each place, and every decision counsel made.

    See the view
  • Security

    The security findings, as a file the scanner you already run can read.

    A whole run
  • Platform

    The declaration in the repo, the project key, and the run exports.

    Keys

Two views
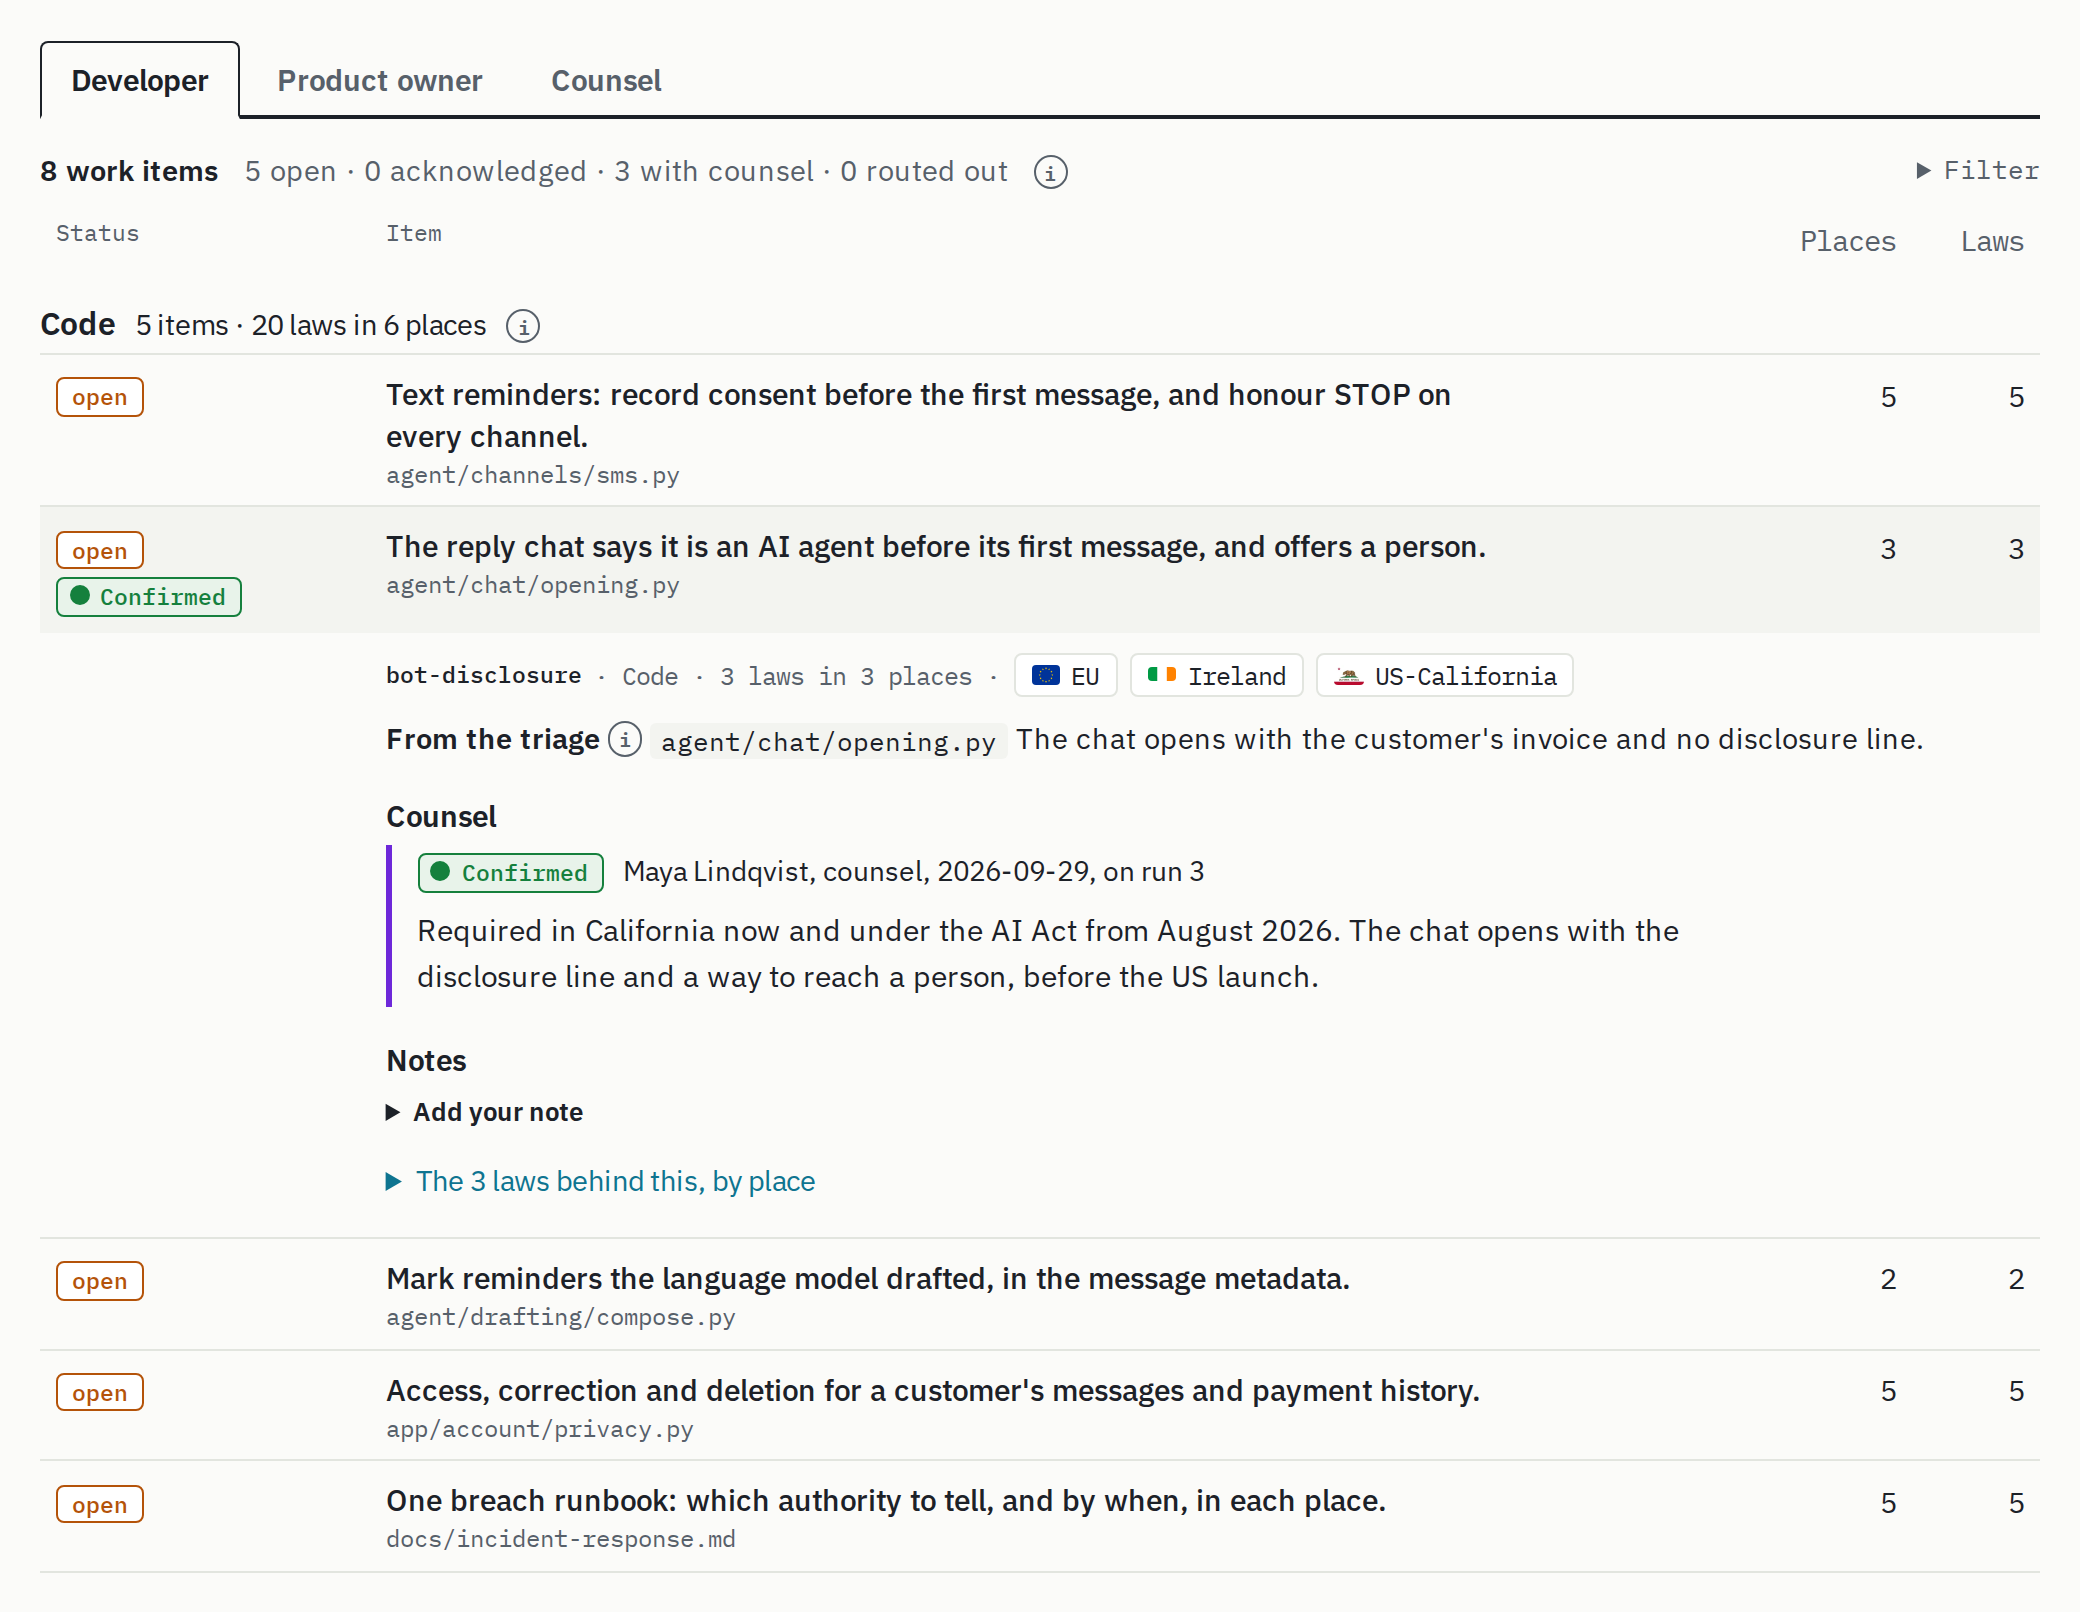
The Developer view of a Pennant run in My LexLint: the worklist, with one item open
Developer: the worklist, one item open.
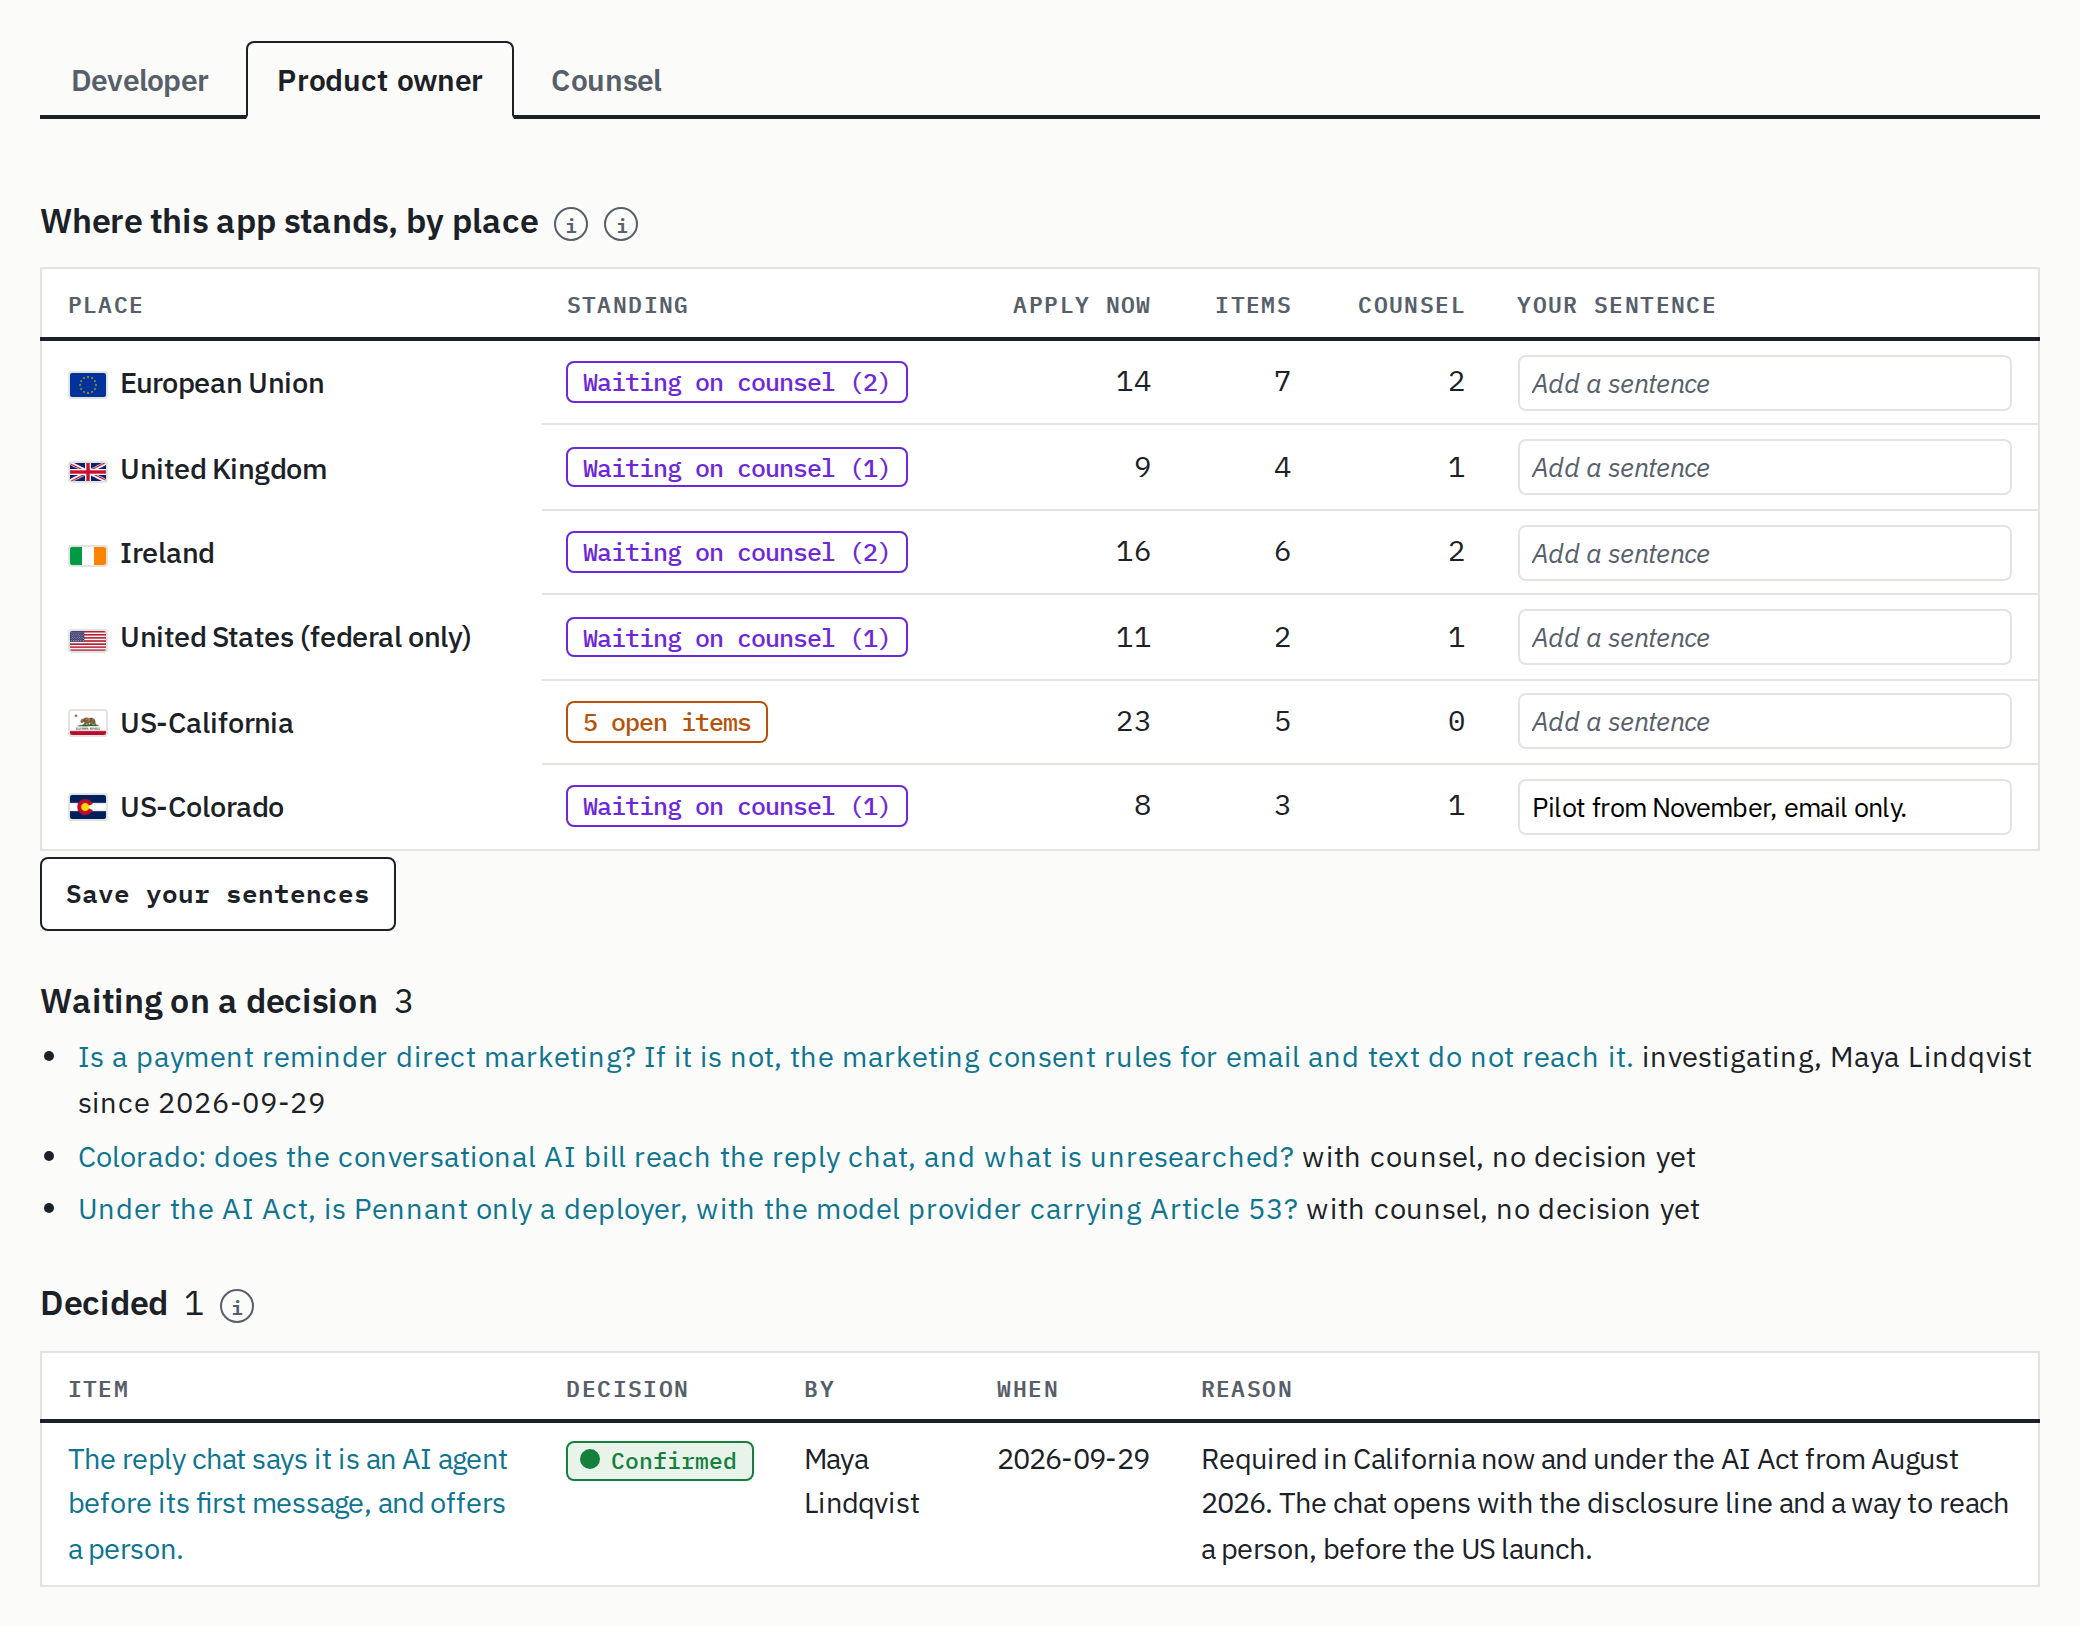
The Product owner view of a Pennant run in My LexLint: where the app stands in each place
Product owner: where Pennant stands, place by place.

From the coding CLI to production In development

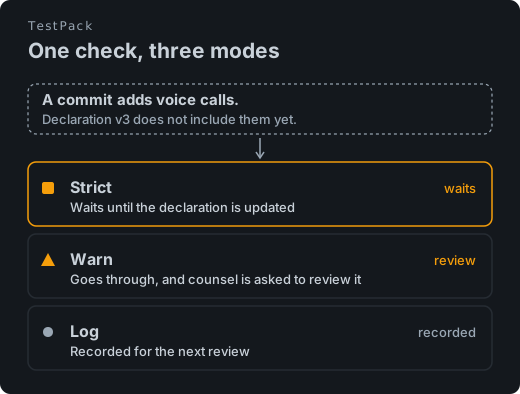
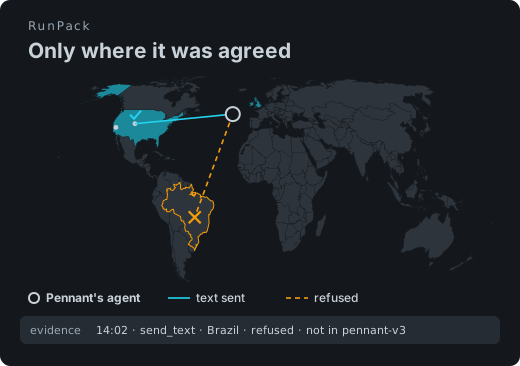
DevPack is the lint in your coding CLI today. TestPack and RunPack check the same declaration in CI and in production.
Start

Your legal team set the project up? Paste the line they sent you, verify it against the code, and send back what you change.

Install LexLint